Who should care: Teams running VPS, VDS or dedicated servers on Contabo, and anyone whose vendors do.
What could go wrong: The VNC console bypasses SSH. If someone else holds that door, your firewall rules stop mattering.
Do this: Set a new VNC password, rotate root and SSH keys, and turn on MFA today.
Worth remembering: “No personal data leaked so far” refers to Contabo’s database. It says nothing about your server.
Contabo, the Munich budget host that passed 500,000 VPS this summer, says an intruder got into its systems over the weekend. In response to the Contabo security incident, the company has reset every customer’s VNC password, and it still can’t say how deep the attacker went.
What Happened in the Contabo Security Incident?
Contabo detected unauthorized access on Saturday, November 14, 2026. It stopped the access, contained it, and called in external incident response specialists for a forensic investigation.
Its fixes show where the worry sits: every VNC password reset, “the known access paths” blocked, internal credentials rotated, and extra monitoring switched on. Contabo published its advisory on November 16.

Contabo sees no sign of leaked personal data “as of now,” but hasn’t said how the attacker got in, what they touched or how long they stayed. Updates post daily at 2pm CET.
What’s the Impact?
VNC is the remote console Contabo gives every VPS and VDS. It sits below the operating system, so it reaches a server even when SSH is locked down. Whoever holds those credentials can reboot into a shell or type commands as if standing at the machine.
That makes the Contabo security incident a question about your own attack surface, not just your host’s. Until Contabo explains the entry point, assume the console was a possible way in.
How to Avoid This
Contabo has done its part. Here is yours after the Contabo security incident:
- Set a fresh VNC password in the Customer Control Panel, even though Contabo already reset it (Contabo’s VNC guide shows where)
- Rotate root passwords, SSH keys, and any API tokens or secrets stored on your servers
- Turn on multi-factor authentication for your Contabo account and every admin login
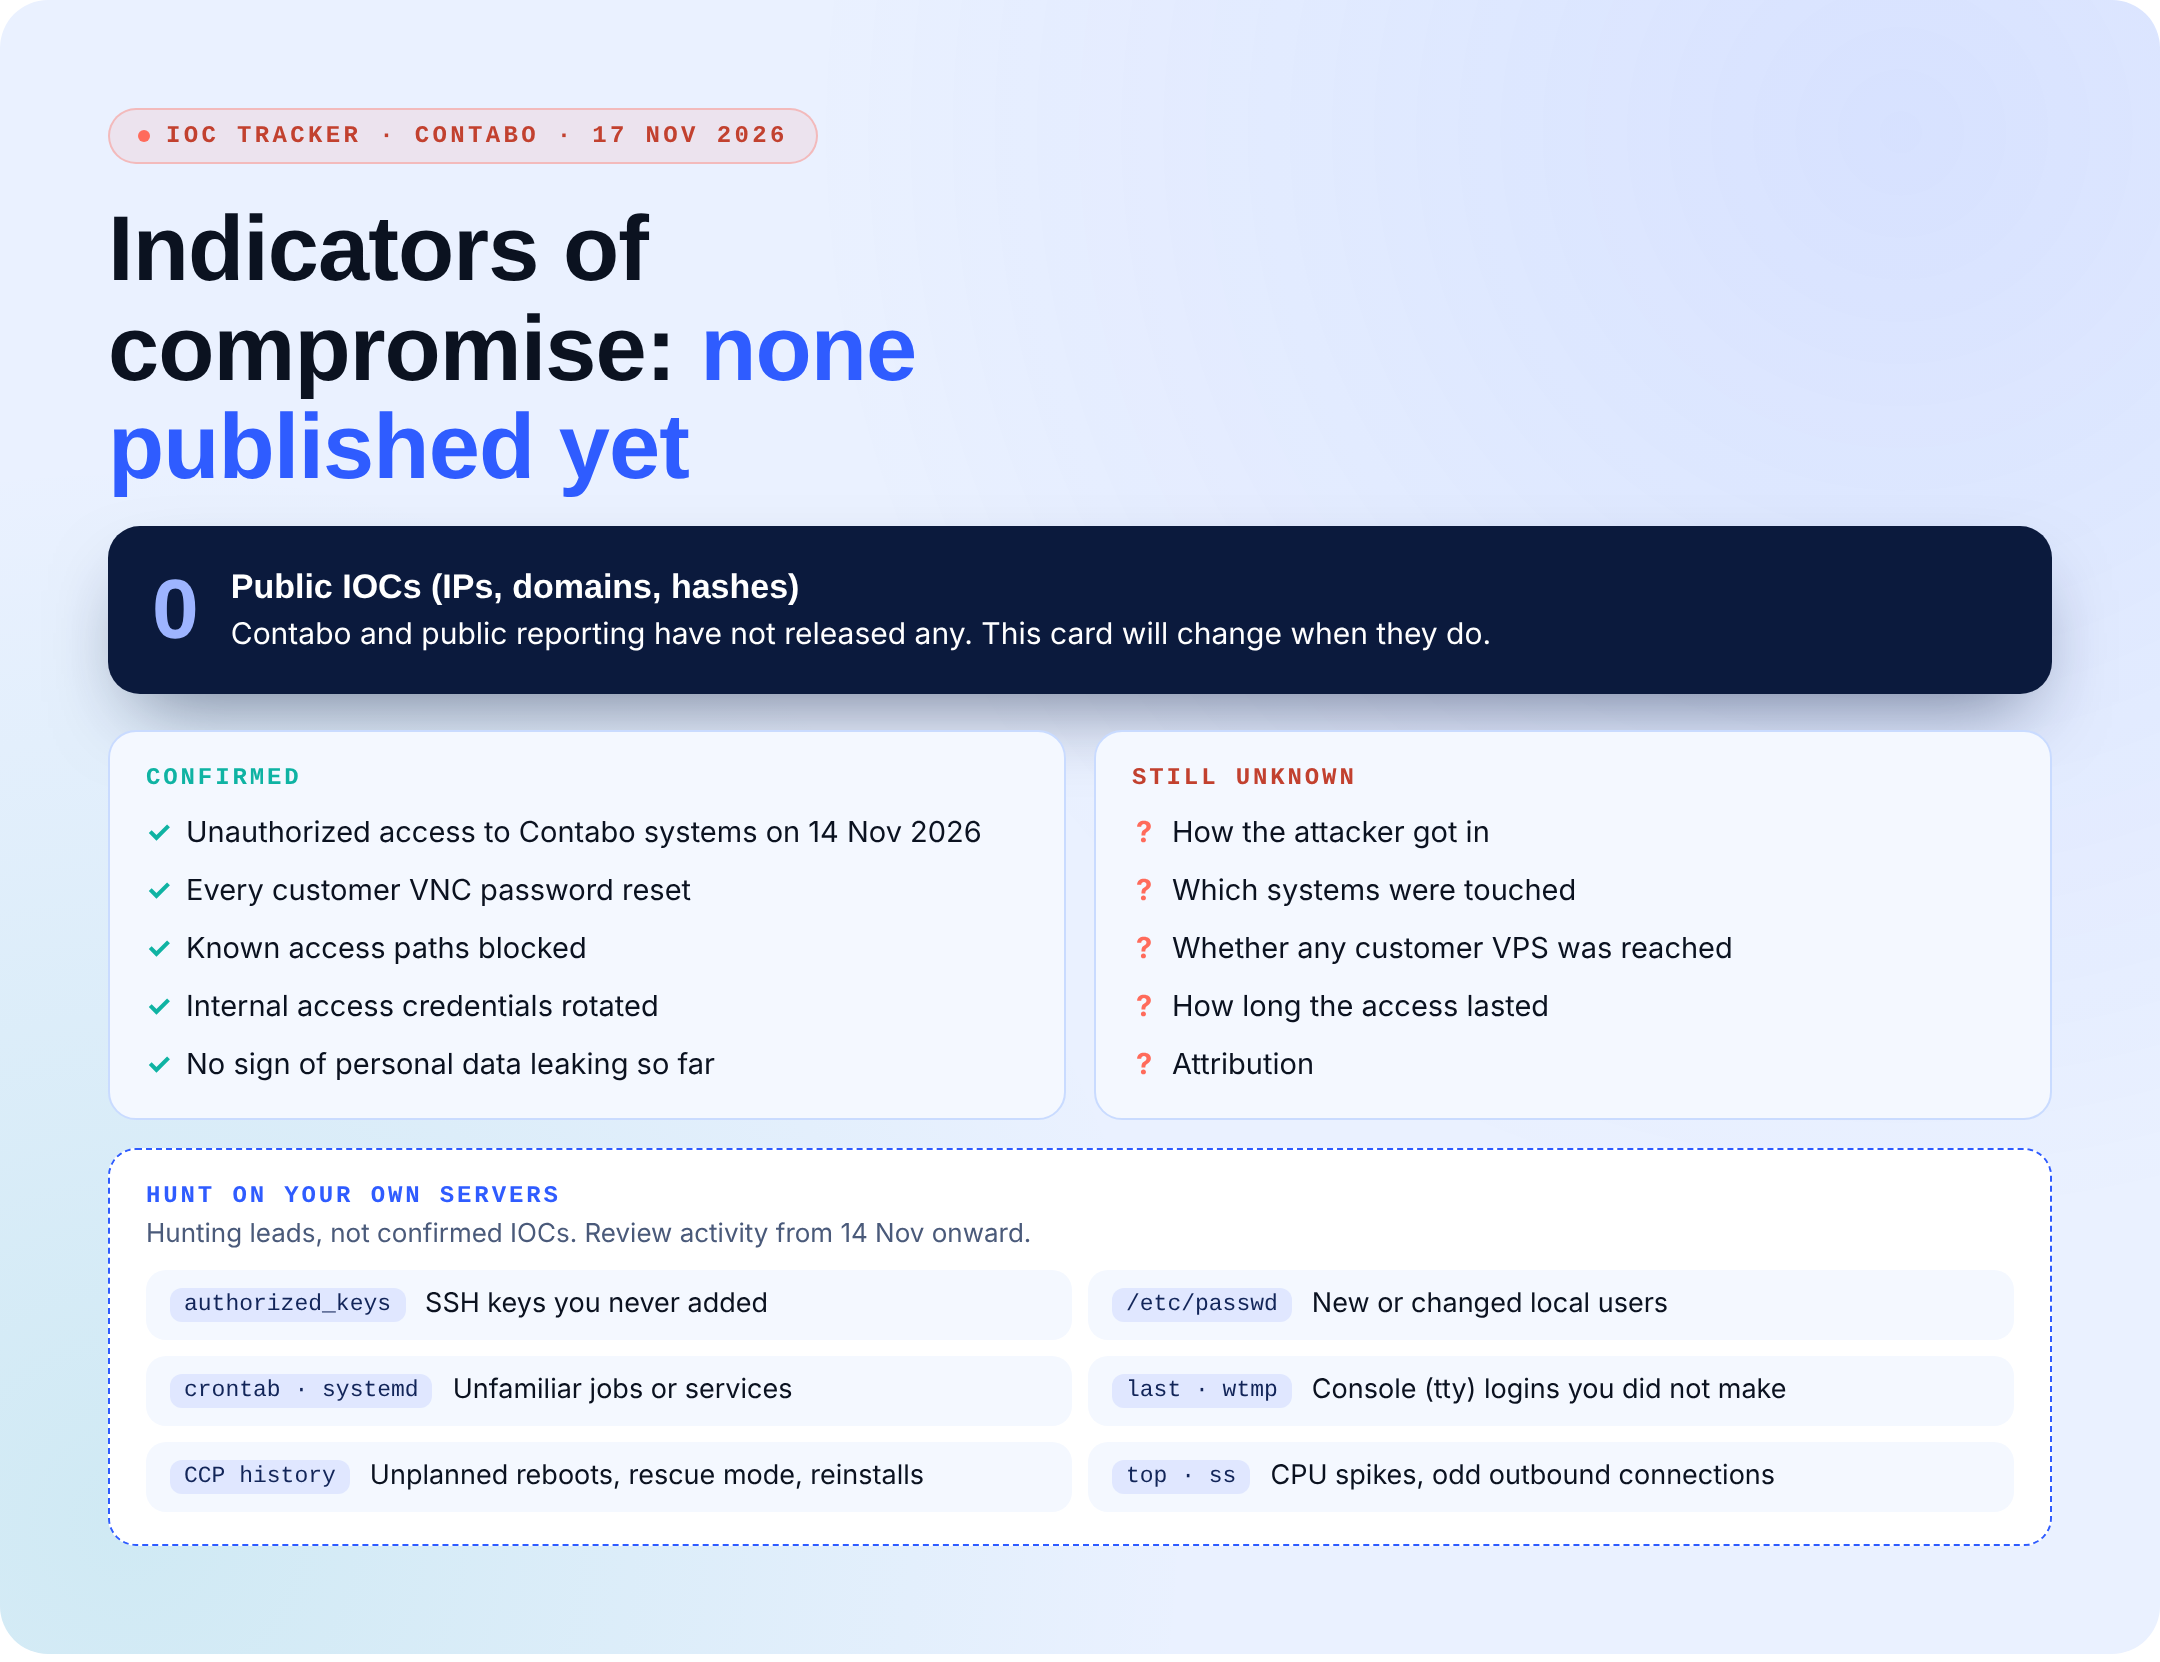
- Review activity from November 14 onward: new users, unknown keys in
authorized_keys, cron jobs, console logins and unplanned reboots - Treat any email about this incident with suspicion and log in to the panel directly
Indicators of Compromise
Neither Contabo nor public reporting has published IOCs (IP addresses, domains or file hashes) for the Contabo security incident as of November 17. We’ll update this story if that changes. Until then, hunt on your own machines using the leads below.
Your Provider Got Hit. Can Attackers Reach You?
A breach at your host is out of your hands. What an attacker can reach on your side of the line isn’t secure.
- Attack your exposed services, including console, SSH, and admin panels, the way a real intruder would
- Flag reused, default, and stale credentials across servers and cloud accounts
- Harden what they find under the rules your team sets, so nothing changes without approval
- Prove every fix with evidence you can hand to leadership or an auditor
- Repeat the cycle every week, so a vendor incident doesn’t turn into a weekend of grunt work
Attack. Harden. Prove. Repeat.