Gootloader Takedown: Police Pull the Plug on the Fake Legal Document Trap
- Who should care: Anyone whose staff search the web for contracts or templates- the lure the Gootloader takedown just cut off. Law firms first.
- What could go wrong: One downloaded “agreement” can put an attacker on your domain controller in under a day.
- Do this: Stop .js files from running out of ZIP archives, today.
- Worth remembering: The servers are gone. The machines already infected are not.
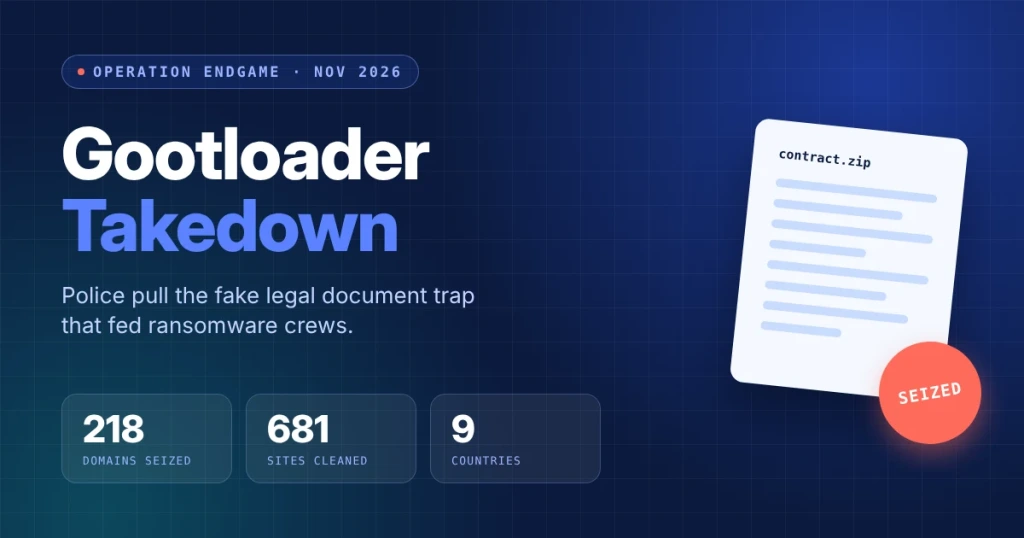
Somebody searches for a sample agreement, clicks a top result and downloads a ZIP. That habit has fed ransomware crews since 2018. This week, the Gootloader takedown took offline the delivery network hiding inside those search results.
What Happened in the Gootloader Takedown?
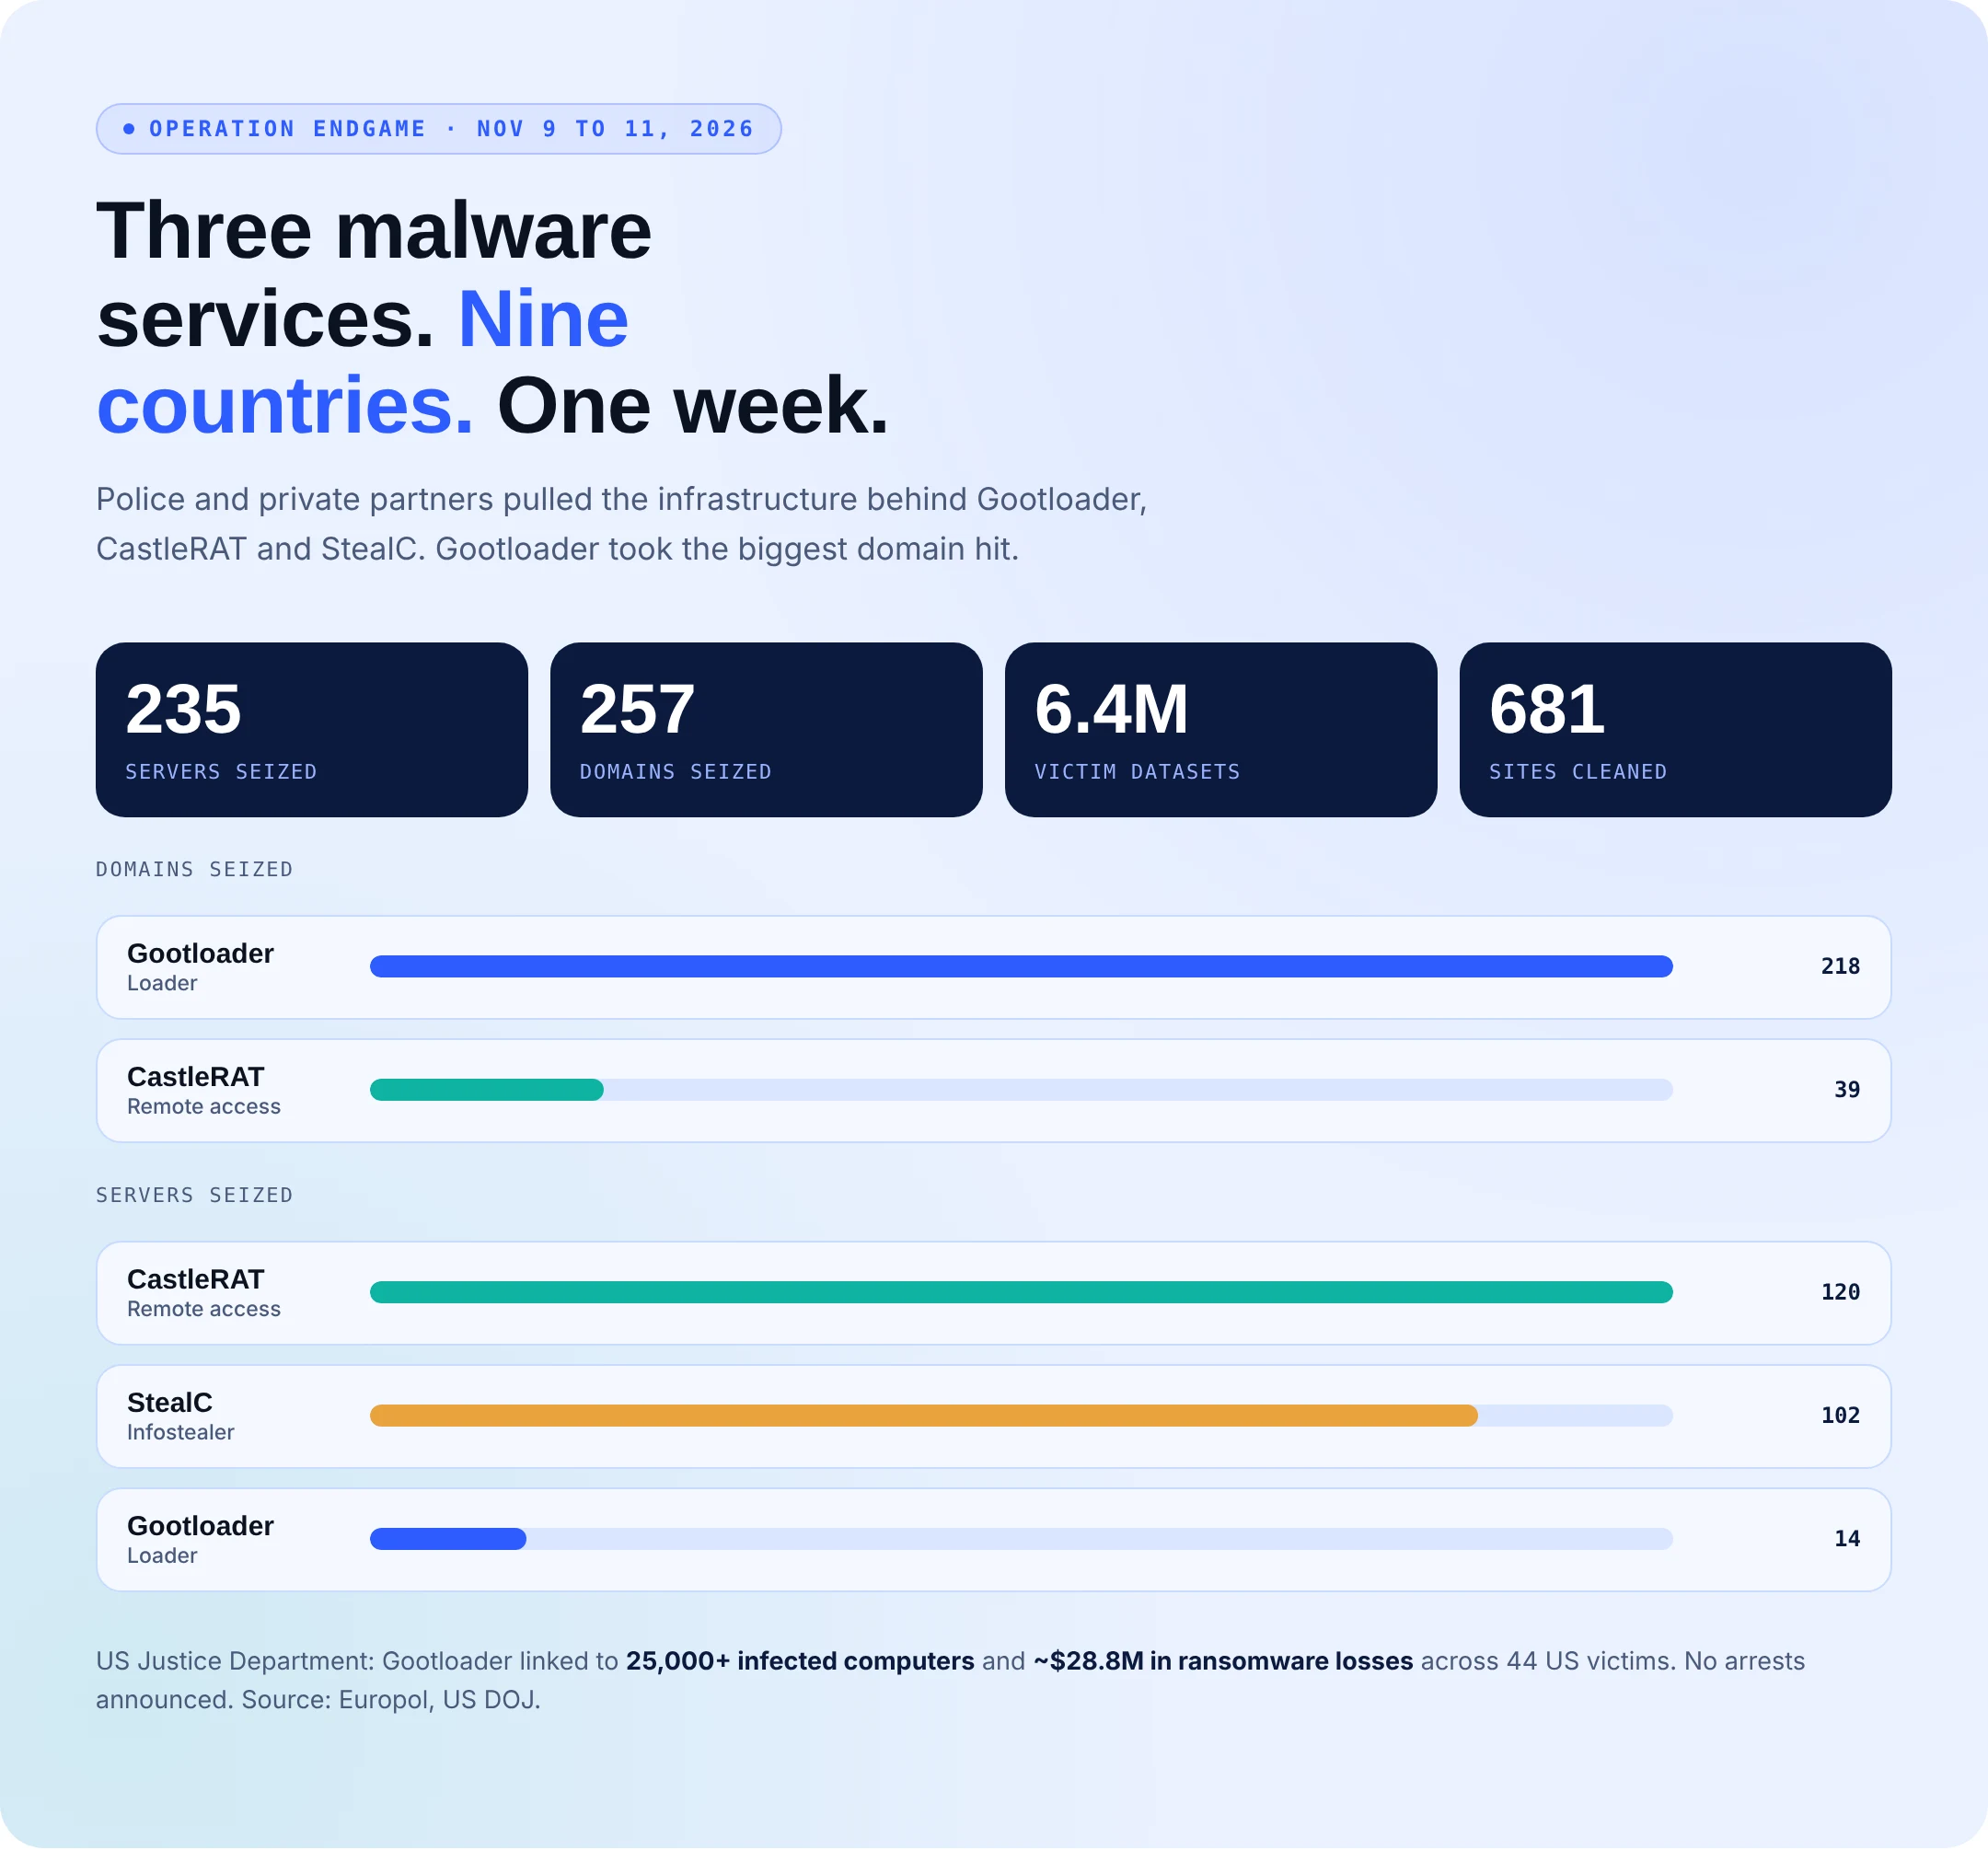
Between November 9 and 11, police from Bulgaria, Canada, Denmark, Germany, Moldova, the Netherlands, Poland, the UK and the US hit three malware services in the latest Operation Endgame round, coordinated by Europol and Eurojust.
The Gootloader takedown hit 14 servers and 218 domains, and responders cleaned 681 compromised websites. CastleRAT lost 120 servers and 39 domains. StealC lost 102 servers. Investigators also recovered 6.4 million stolen victim datasets, Help Net Security reported.
The US Justice Department said it removed Gootloader from more than 100 servers, many of them hijacked WordPress sites, according to BleepingComputer. No arrests were announced.
How the Trap Worked
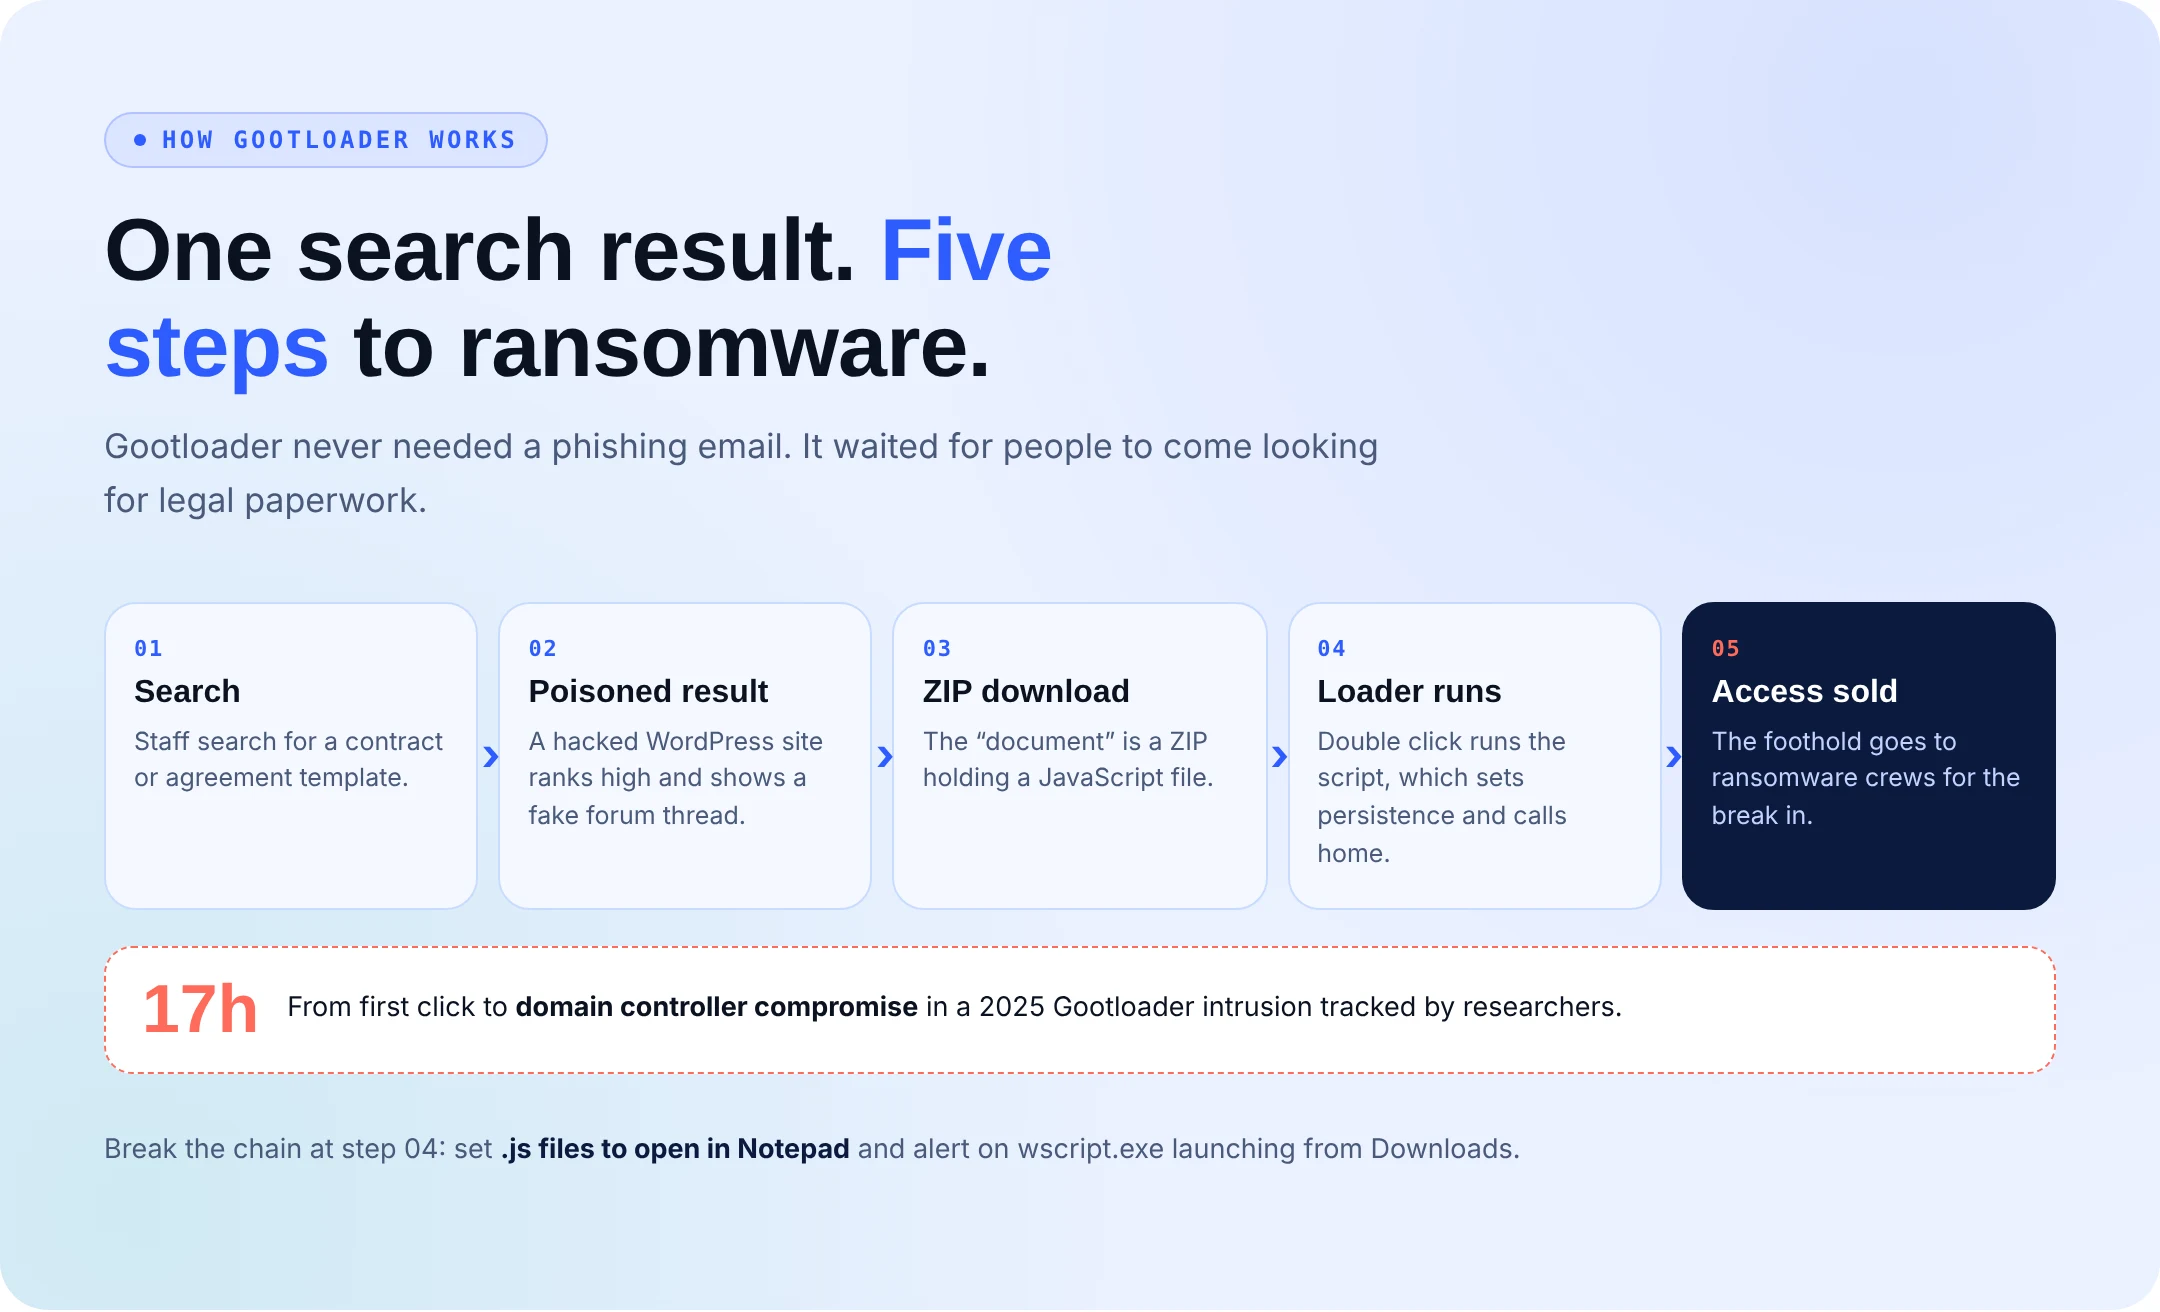
Gootloader runs on SEO poisoning. Operators plant fake forum threads on hacked WordPress sites, rank them for legal template searches, and serve a ZIP holding a JavaScript file. Open it, and ransomware affiliates buy the foothold.
In one 2025 case analyzed by Huntress, attackers reached a domain controller within 17 hours.
What’s the Impact?
The Justice Department ties Gootloader to at least 25,000 infected computers worldwide and ransomware attacks on 44 US victims, with about $28.8 million in losses.
The Gootloader takedown stops new infections from these servers. Stolen credentials are another story. They get resold and reused for the next break-in, long after the servers go dark.
Gootloader Takedown Indicators of Compromise
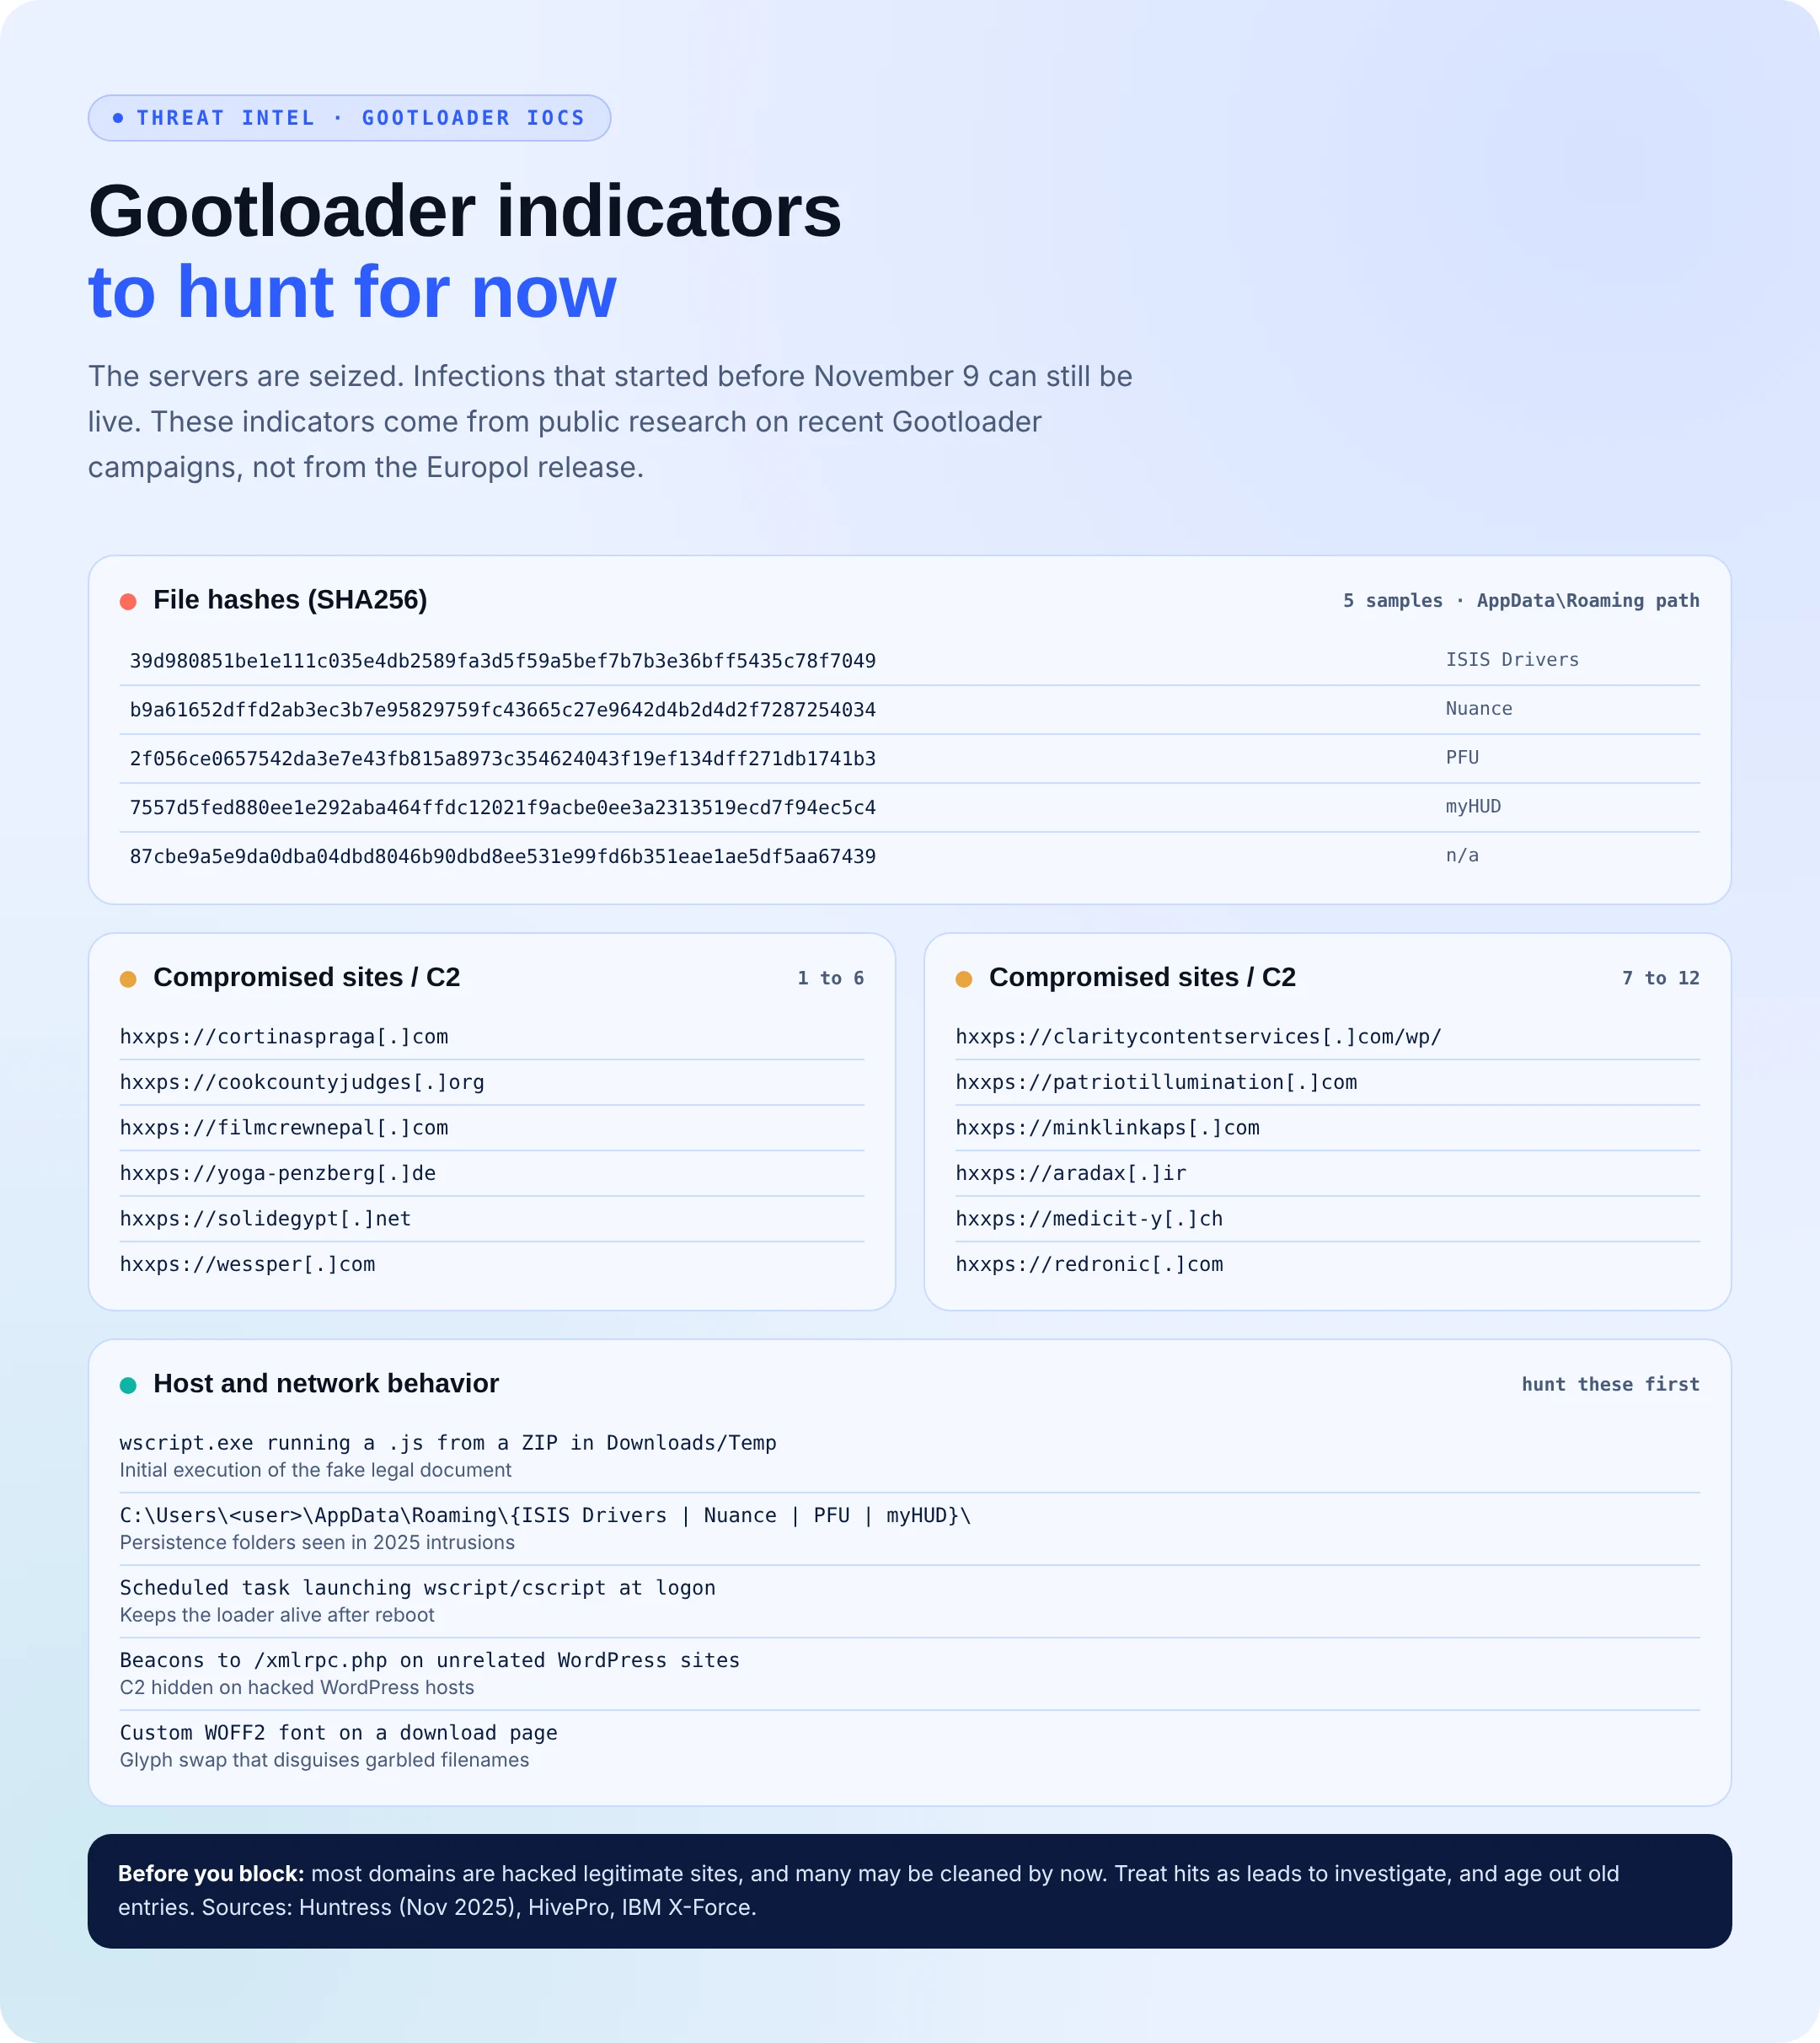
Neither agency published indicators. The IOC card below pulls hashes, compromised domains and host artifacts from public research on recent Gootloader campaigns. Use it to hunt for older infections, and treat matches as leads to investigate.
How to Avoid This
- Set .js and .jse files to open in Notepad, so a double-click cannot run them.
- Alert when wscript.exe or cscript.exe runs a script from Downloads or Temp folders.
- WordPress admins: rotate credentials, turn on MFA, and patch plugins, as Europol advised.
- Hunt for new scheduled tasks and odd folders under AppData\Roaming created after a ZIP download.
- Check Have I Been Pwned and similar services for exposed company accounts.
Police Took the Servers. Your Exposure Stayed Behind.
The Gootloader takedown removed infrastructure. It did not remove footholds already inside your network or credentials already sold. Secure.com’s AI teammates attack your defenses the way a loader crew would, harden what they find and prove the fix, while your team sets the rules.
- Red Teammate replays the search, download and script chain to show whether a fake contract would run on your endpoints.
- SOC Teammate sweeps the fleet for the indicators above and builds the case.
- Exposure checks flag company logins that show up in stealer data before anyone uses them.
- Containment stays reversible and waits for human approval under rules you write.
- Every fix gets retested, so “patched” comes with proof. Attack. Harden. Prove. Repeat.
The Bottom Line
Endgame bought defenders time. Spend it finding the infections a seizure could never reach.
Related Articles on Secure.com
- Vidar Infostealer Tops the Chaotic Cybercrime Market After Lumma’s Collapse
- Operation Olympus Blade: Inside the Kratos Takedown