Able2Shell Puts N-central Exploits Online, and the Fix Is Only Half the Job
Who should care: Any business whose IT provider runs its computers through N-central, and any provider that does.
What could go wrong: Someone who can reach the management screen could take it over without a password and reach every computer it manages.
Do this: Install the emergency fix, then update the agent on every managed computer, and keep the screen off the internet.
Worth remembering: The Able2Shell hotfix closes the server, not the exposure. You’re done when you have updated every managed computer and checked the days before the fix.
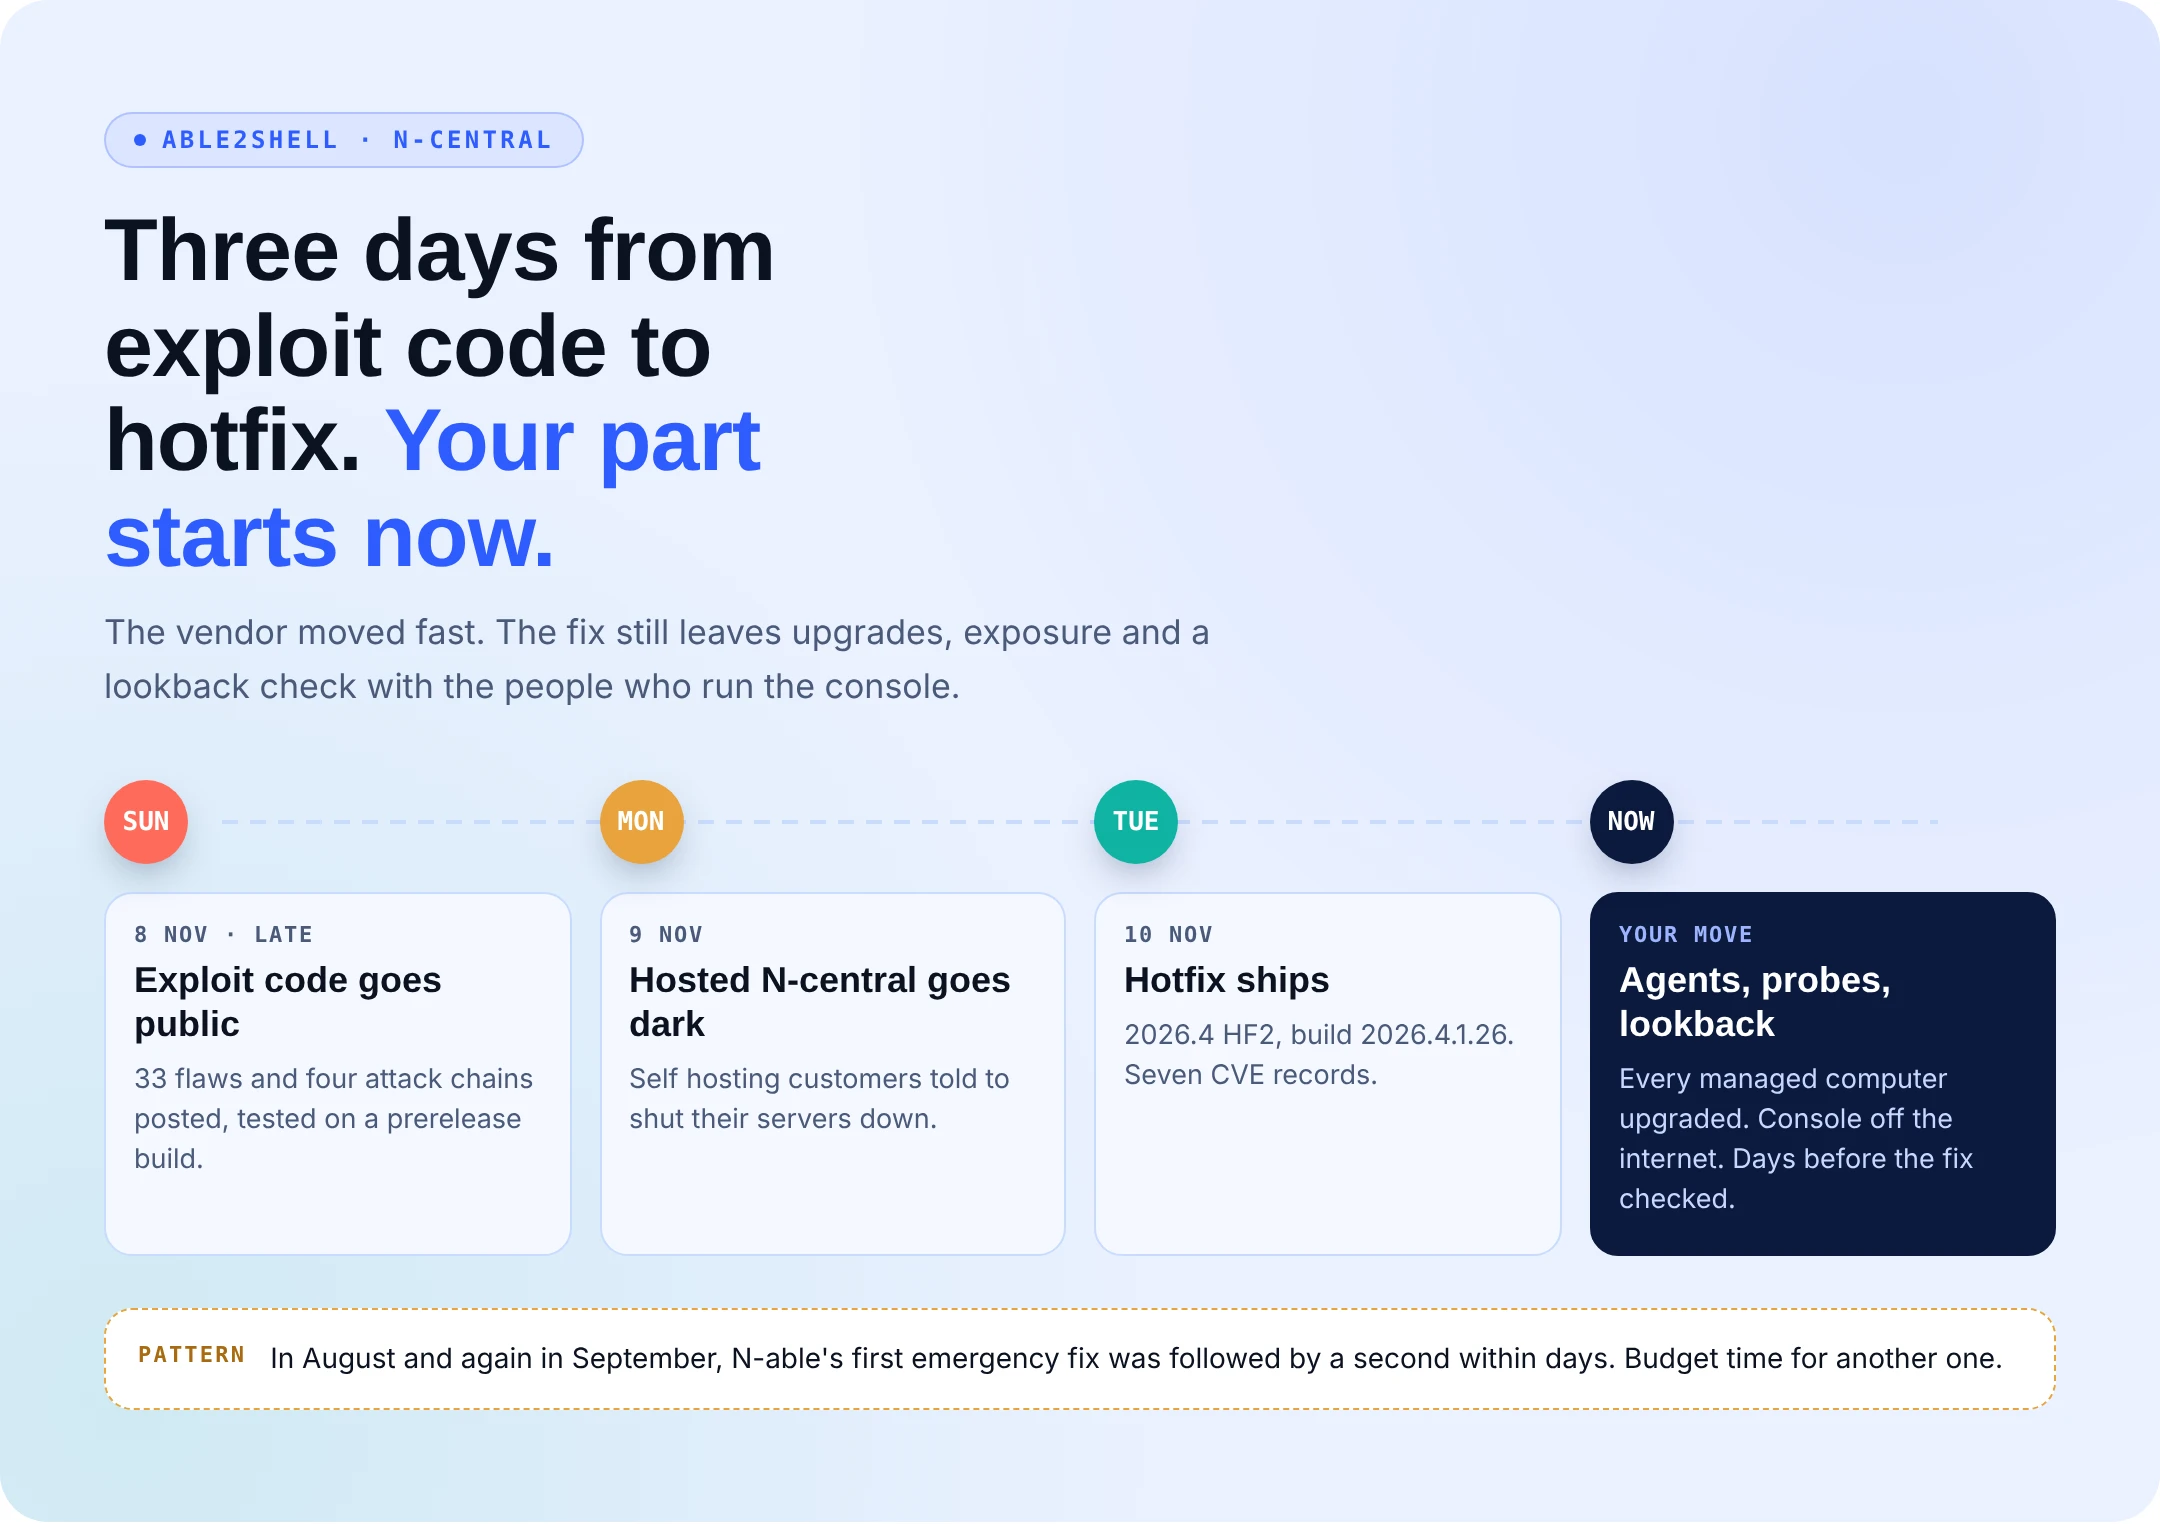
On Sunday night, a researcher published working attack code for more than 30 flaws in N-central, the tool IT providers use to control and patch customer computers. The release, called Able2Shell, pushed N-able to pull its hosted version Monday and ship an emergency fix Tuesday.
What Happened With Able2Shell?
Late on 8 November, a public GitHub repository went up with 33 flaws, four attack chains and the code to run them. Three chains end in remote code execution; one ends in root access. The researcher tested them on a prerelease build and says most, if not all, should work on earlier versions.
By Monday, N-able had taken hosted N-central offline and told self-hosting customers to shut down their servers. On Tuesday, it shipped N-central 2026.4 HF2 (build 2026.4.1.26), according to its release notes.
N-able says it has seen scanning but no evidence that attackers successfully broke into any customer environment. Huntress says it has seen none among its partners.
What’s the Impact?
N-central sits above every computer a provider manages. An attacker who uses Able2Shell to take the console inherits that reach: scripts, remote sessions and software installs across many client networks at once. That is a large blast radius for a single login screen. One weak console becomes the problem of every business behind it, including ones that never picked the tool.
Why “Patched” Isn’t the Finish Line
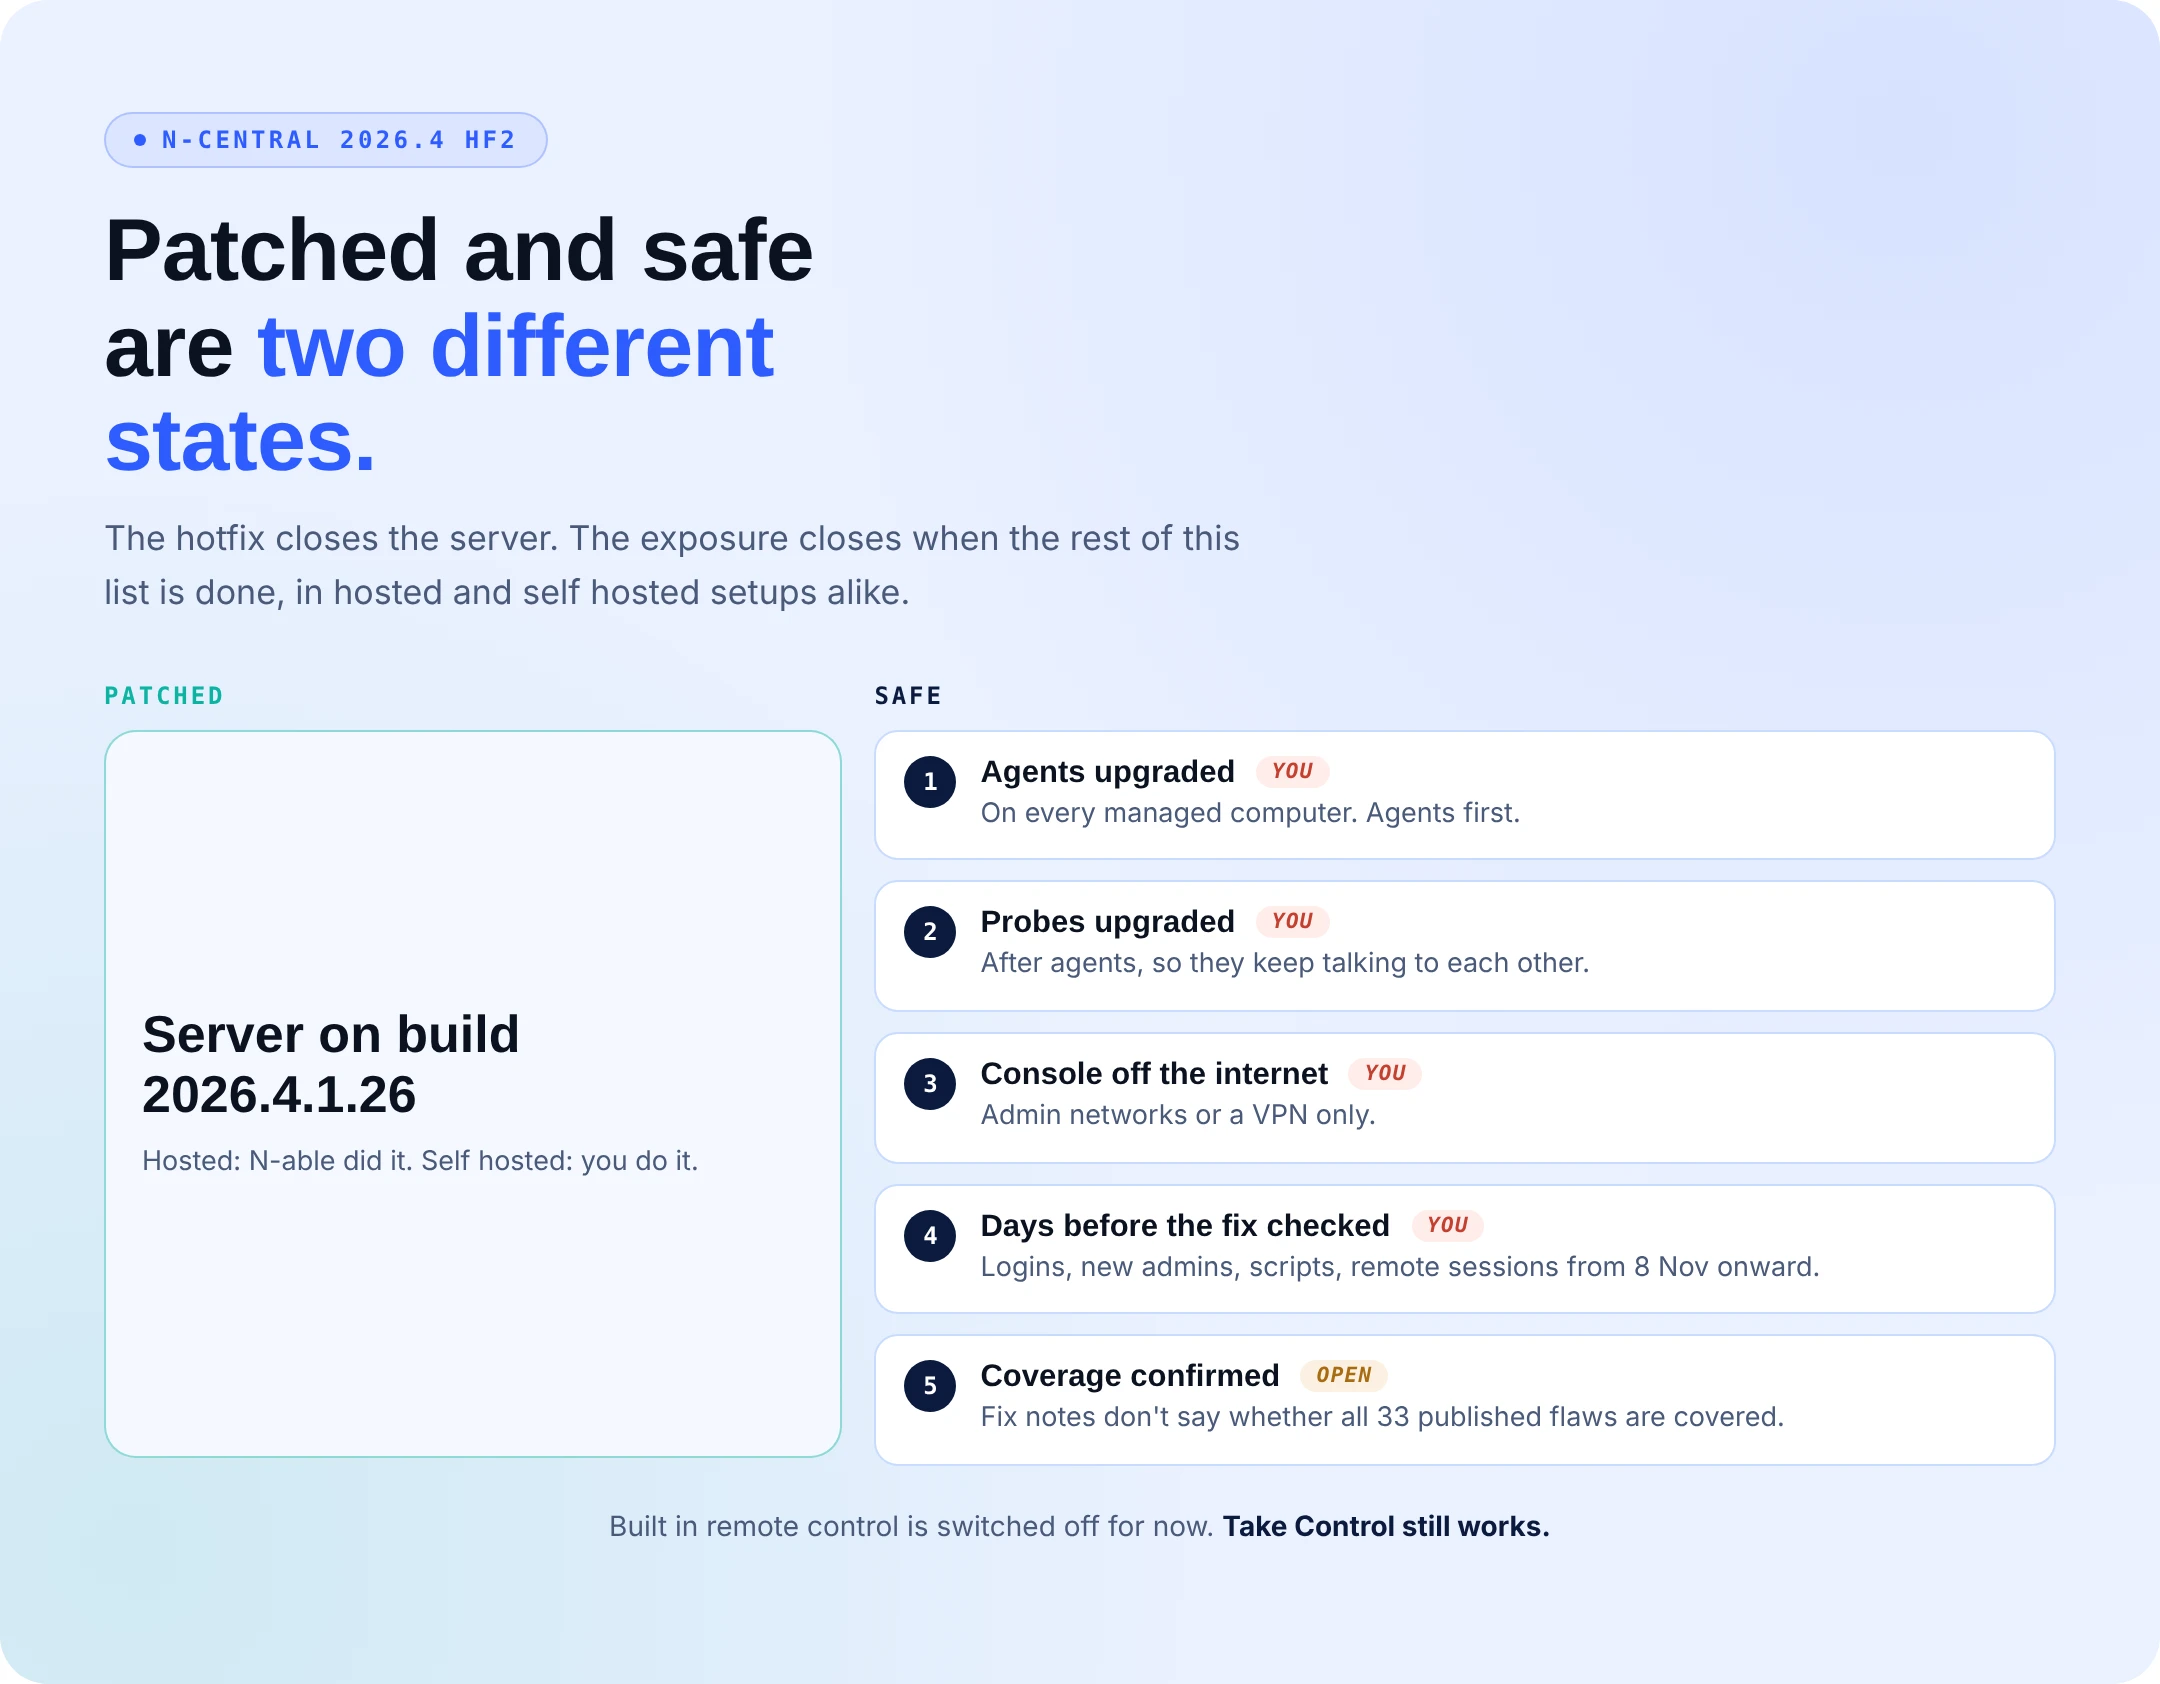
The fix is three jobs. N-able upgrades hosted servers, but every customer, hosted or not, has to upgrade agents first and probes second. N-able has switched off built-in remote control for now, though Take Control still works.
Two more gaps keep this open. N-able’s fix notes do not say whether HF2 covers all 33 published flaws. And there’s a pattern: in August and again in September, N-able shipped a second emergency fix within days of the first. Until you validate the exposure is actually closed, treat Able2Shell as live.
How to Avoid This
- Self-hosting? Install 2026.4 HF2 today. Hosted servers are already done.
- Upgrade agents on every managed computer, then probes.
- Keep the console off the public internet. Admin networks or a VPN only.
- Review logins, new admin accounts, scripts, and remote sessions from 8 November until the moment you patched.
- Watch for a follow-up hotfix and apply it the same day.
If Your IT Provider Runs N-central, Ask Them
- Is our console on HF2, and are the agents on our computers up to date?
- Can anyone reach the console from the internet?
- Has anyone checked activity from the days before the fix?
For Your Security Team
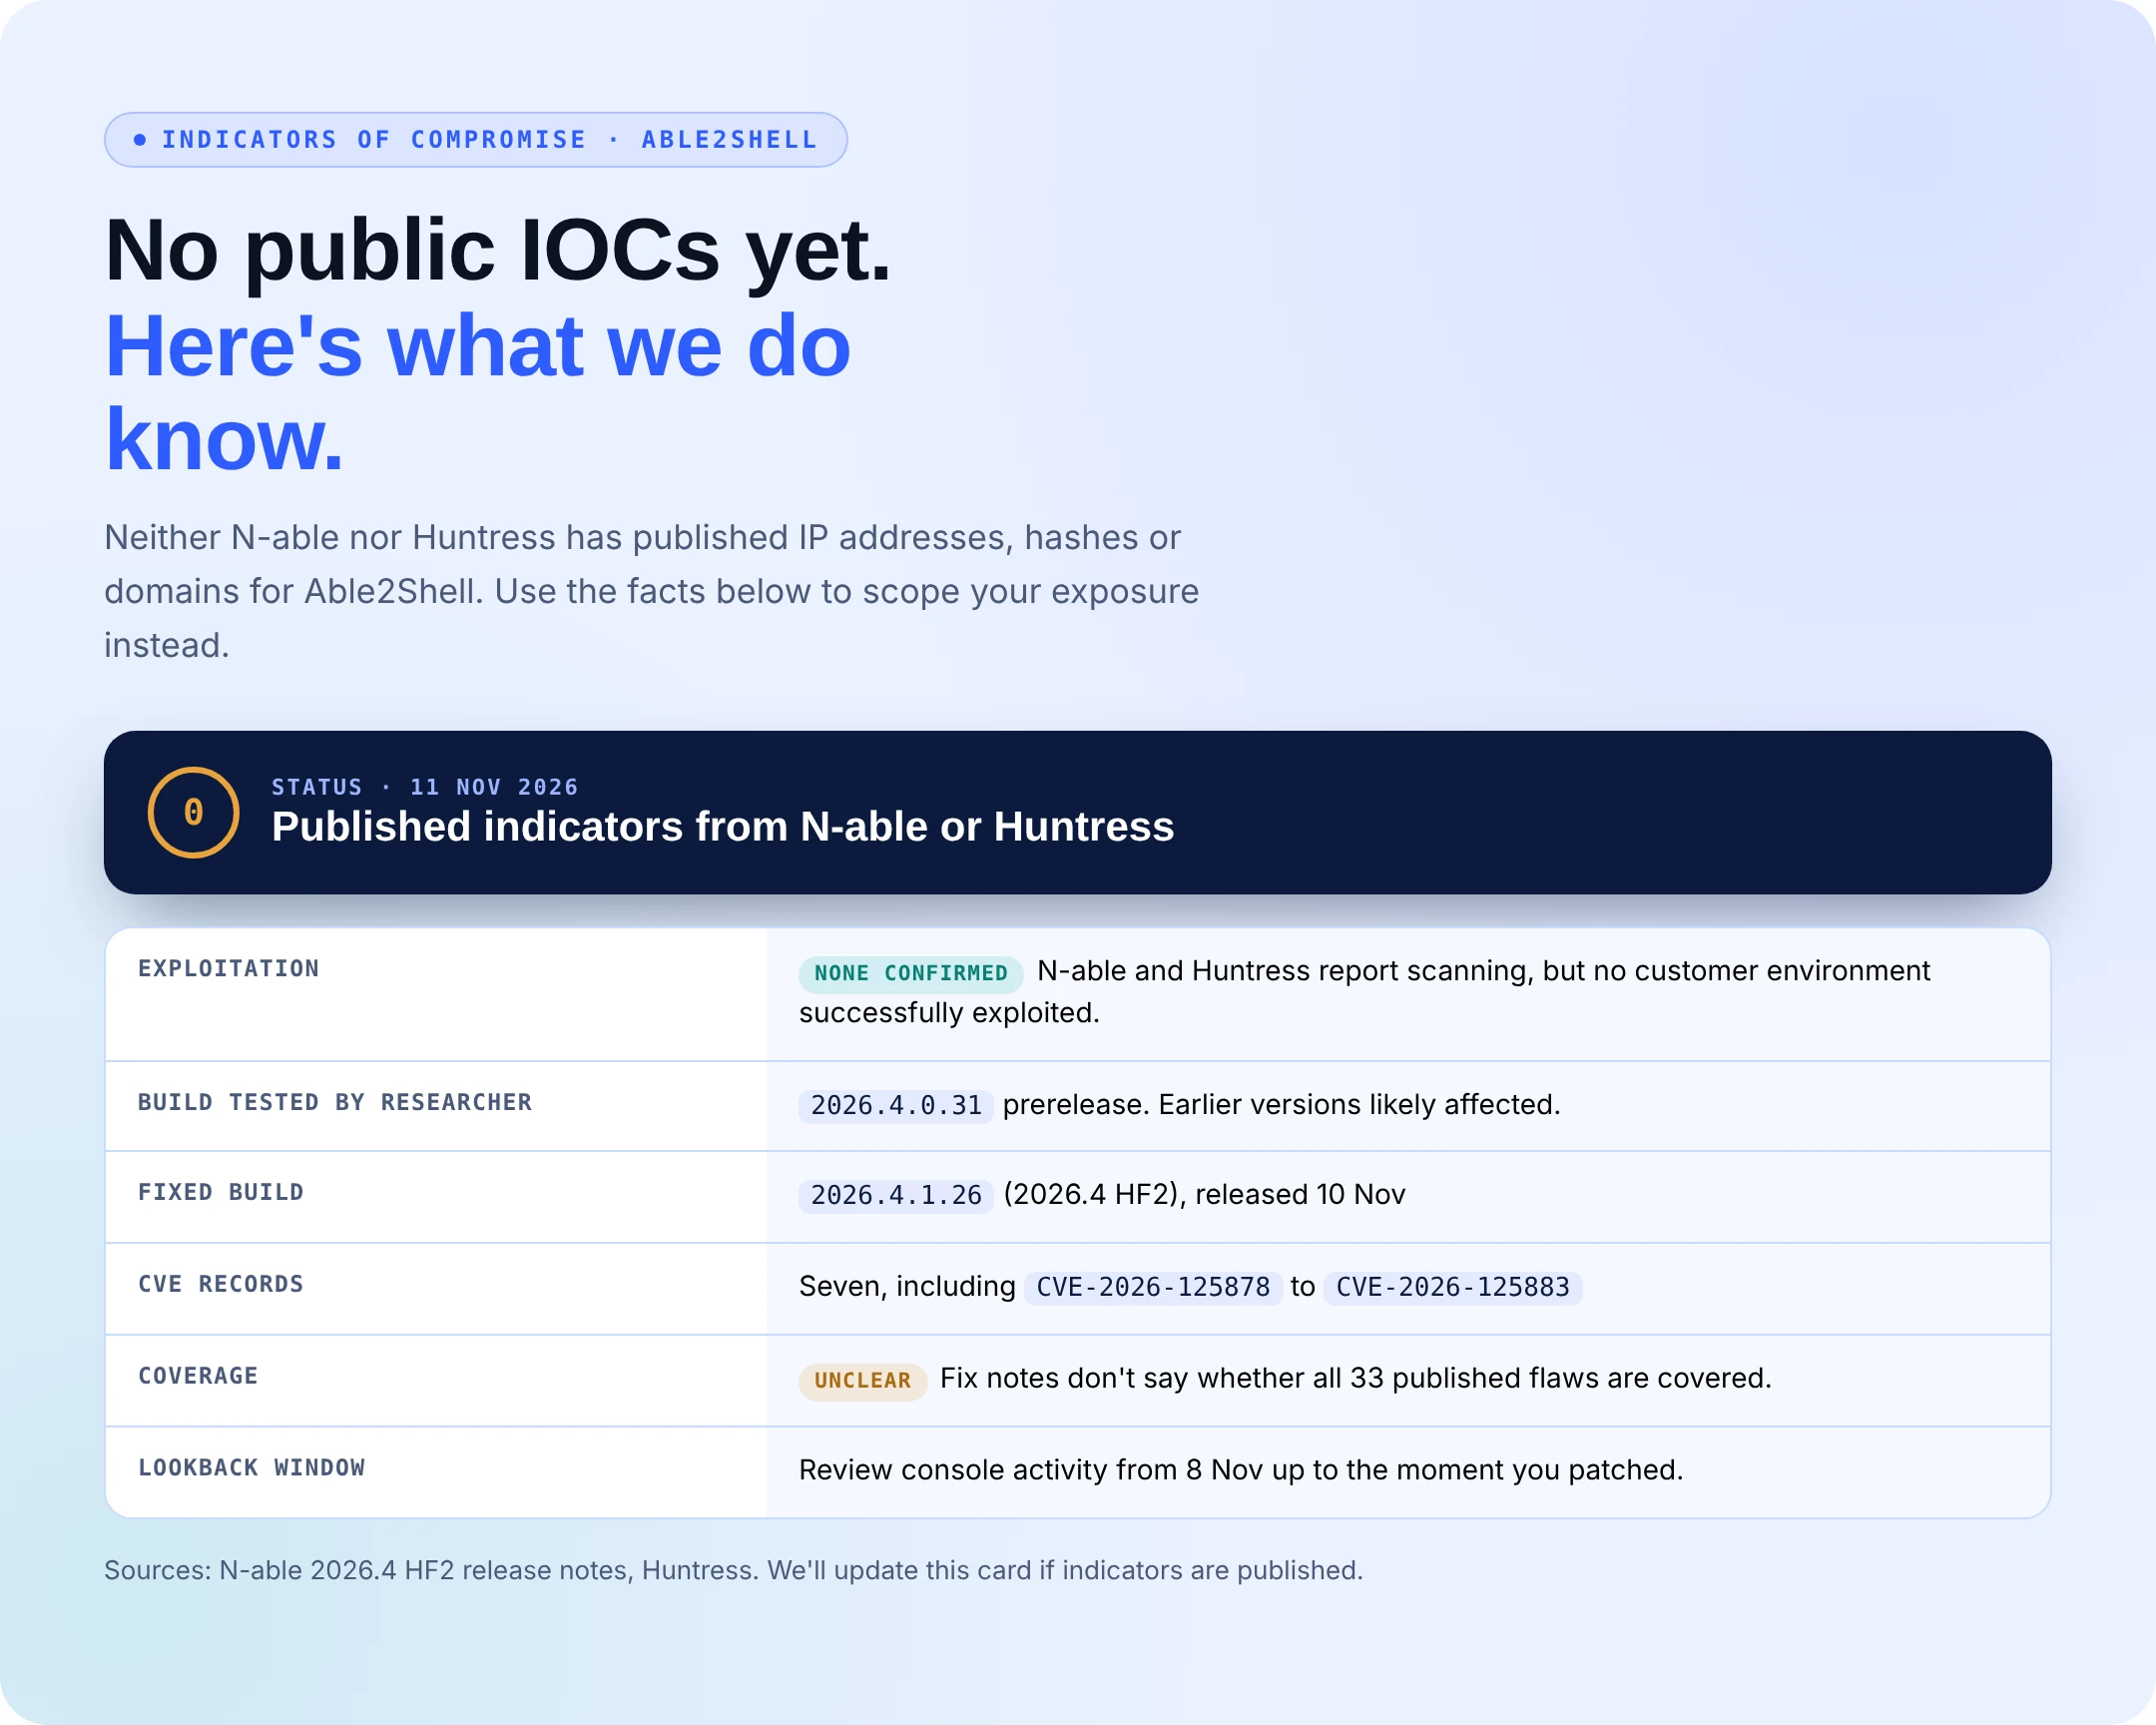
- Fixed build: N-central 2026.4 HF2, build 2026.4.1.26, released 10 November with seven CVE records, including CVE-2026-125878 through CVE-2026-125883.
- Researcher’s test target: N-central Appliance 2026.4.0.31, a prerelease build. “33” is the researcher’s count.
- Indicators: N-able and Huntress have not published any indicators of compromise.
- Credit: Sean Bales found and published the Able2Shell flaws. Sprocket Security’s Nate Fair earned credit for CVE-2026-125882.
Able2Shell FAQs
What is Able2Shell?
Which N-central version fixes the flaws?
Has anyone exploited the flaws yet?
Is installing the hotfix enough?
Are there any indicators of compromise?
Related reading from Secure.com: