November 11, 2026
- Who should care: Anyone with internet-facing apps, APIs, Microsoft 365 tenants, or cloud storage.
- What could go wrong: An AI agent finds your exposed admin panel at 3 a.m., and nobody is awake to notice.
- Do this: Lock down unauthenticated APIs and rotate any secret sitting in frontend code.
- Worth remembering: A full campaign costs as little as $145 in AI model fees.
Introduction
The ARTEX AI pen test tool was built to help defenders. It has turned into a cheap, tireless hacker. Fresh research shows criminals setting a goal, walking away, and letting AI agents do the breaking in.
What Happened?
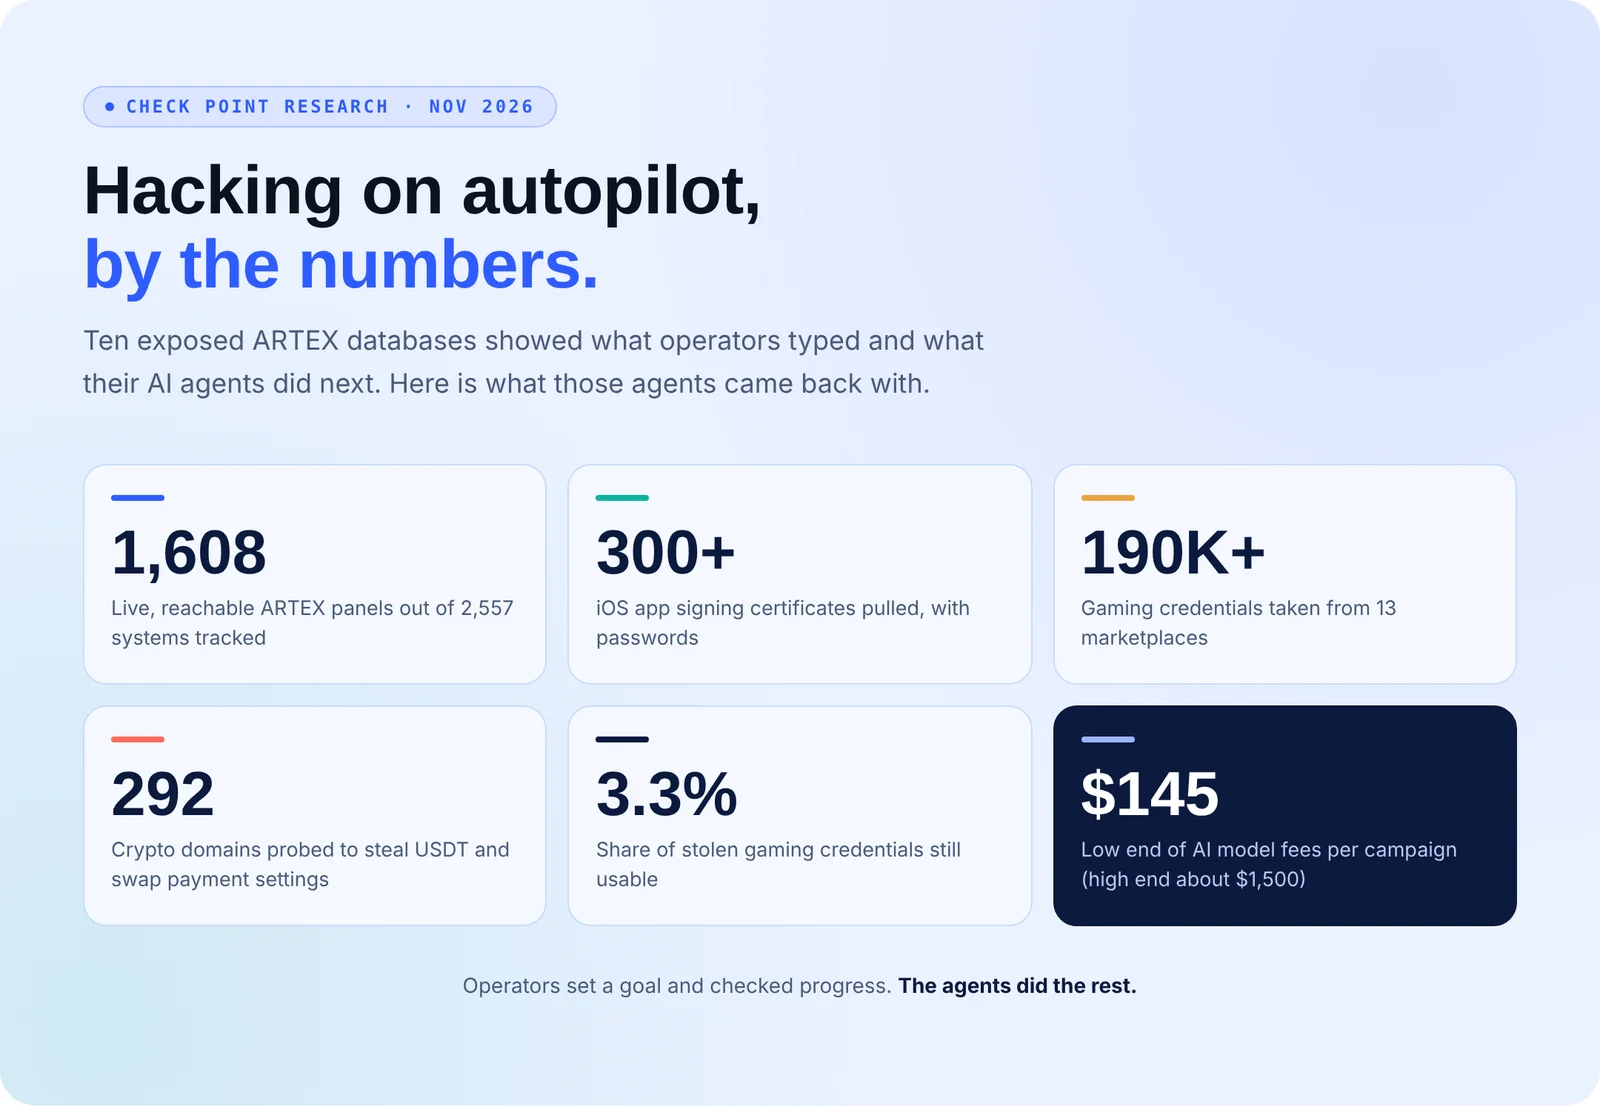
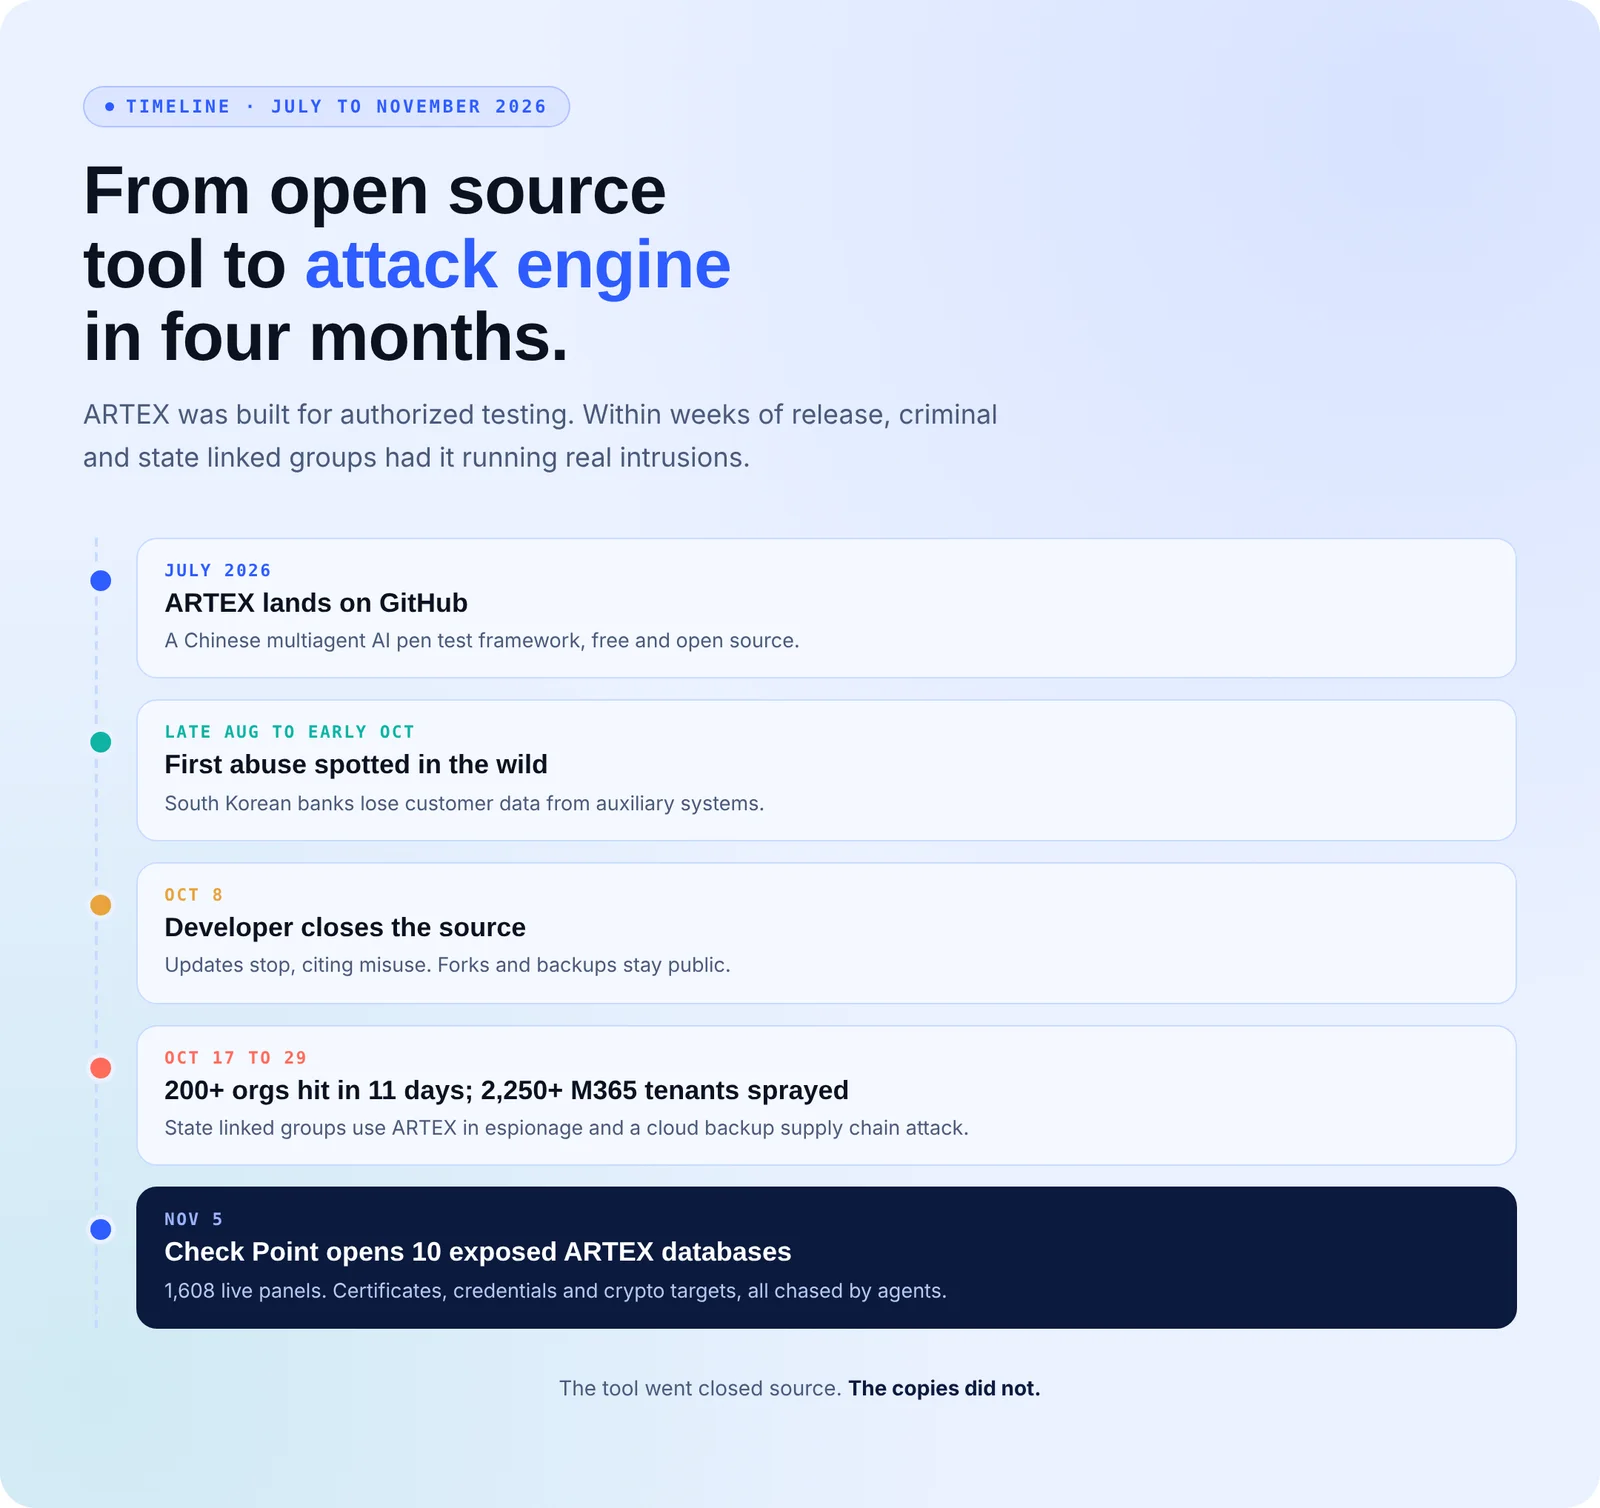
ARTEX, a Chinese multi-agent penetration testing framework, landed on GitHub in July 2026. On November 5, Check Point Research counted 2,557 systems that had hosted ARTEX panels, 1,608 of them live and reachable. Ten misconfigured instances exposed their full databases. They showed exactly what operators typed into the ARTEX AI pen test tool and what its agents did next.
Three campaigns stood out. Agents pulled more than 300 iOS app signing certificates with passwords and 190,000+ gaming credentials from 13 marketplaces. They also probed 292 crypto domains to steal USDT and swap payment settings. One open API leaked AWS keys with write access to an S3 bucket, and agents altered download files.
The Impact
Running a campaign with the ARTEX AI pen test tool cost roughly $145 to $1,500 in model fees. That price tag changes who can attack. State-linked groups use ARTEX too. One campaign hit 200+ organizations in 14 countries in 11 days, and another sprayed logins at more than 2,250 Microsoft 365 tenants, according to Infosecurity Magazine.
Reality Check
Not everything worked. Only about 3.3% of the gaming credentials stayed usable, and some “cashouts” the agents reported were hallucinations. No stolen funds reached the attacker’s wallet. Still, an attacker who can retry around the clock only needs a few hits. The developer closed the source on October 8, yet forks of the ARTEX AI pen test tool are still public.
How to Avoid This
- Put authentication on every API and pull admin panels off the public internet.
- Scan frontend code and deployed files for keys, then rotate anything you find.
- Restrict who can change downloads, manifests, and landing pages, and alert on edits.
- Revoke tokens and sessions during incident response, not only passwords.
- Alert on login bursts spaced exactly one second apart.
Let Your Own AI Hit You First
Attackers now rent offense by the hour. The fix is to run it on yourself, under your rules, before someone else does.
- Secure.com AI Teammates attack your exposed apps, APIs, and identity paths the same way agents in the ARTEX AI pen test tool do.
- Every finding becomes a ranked fix list tied to the asset owner.
- Your team sets the scope and approves anything disruptive. AI Teammates do the work.
- Retests prove each fix held, with audit-ready evidence.
- No more grunt work, no more burnout.
Attack. Harden. Prove. Repeat.
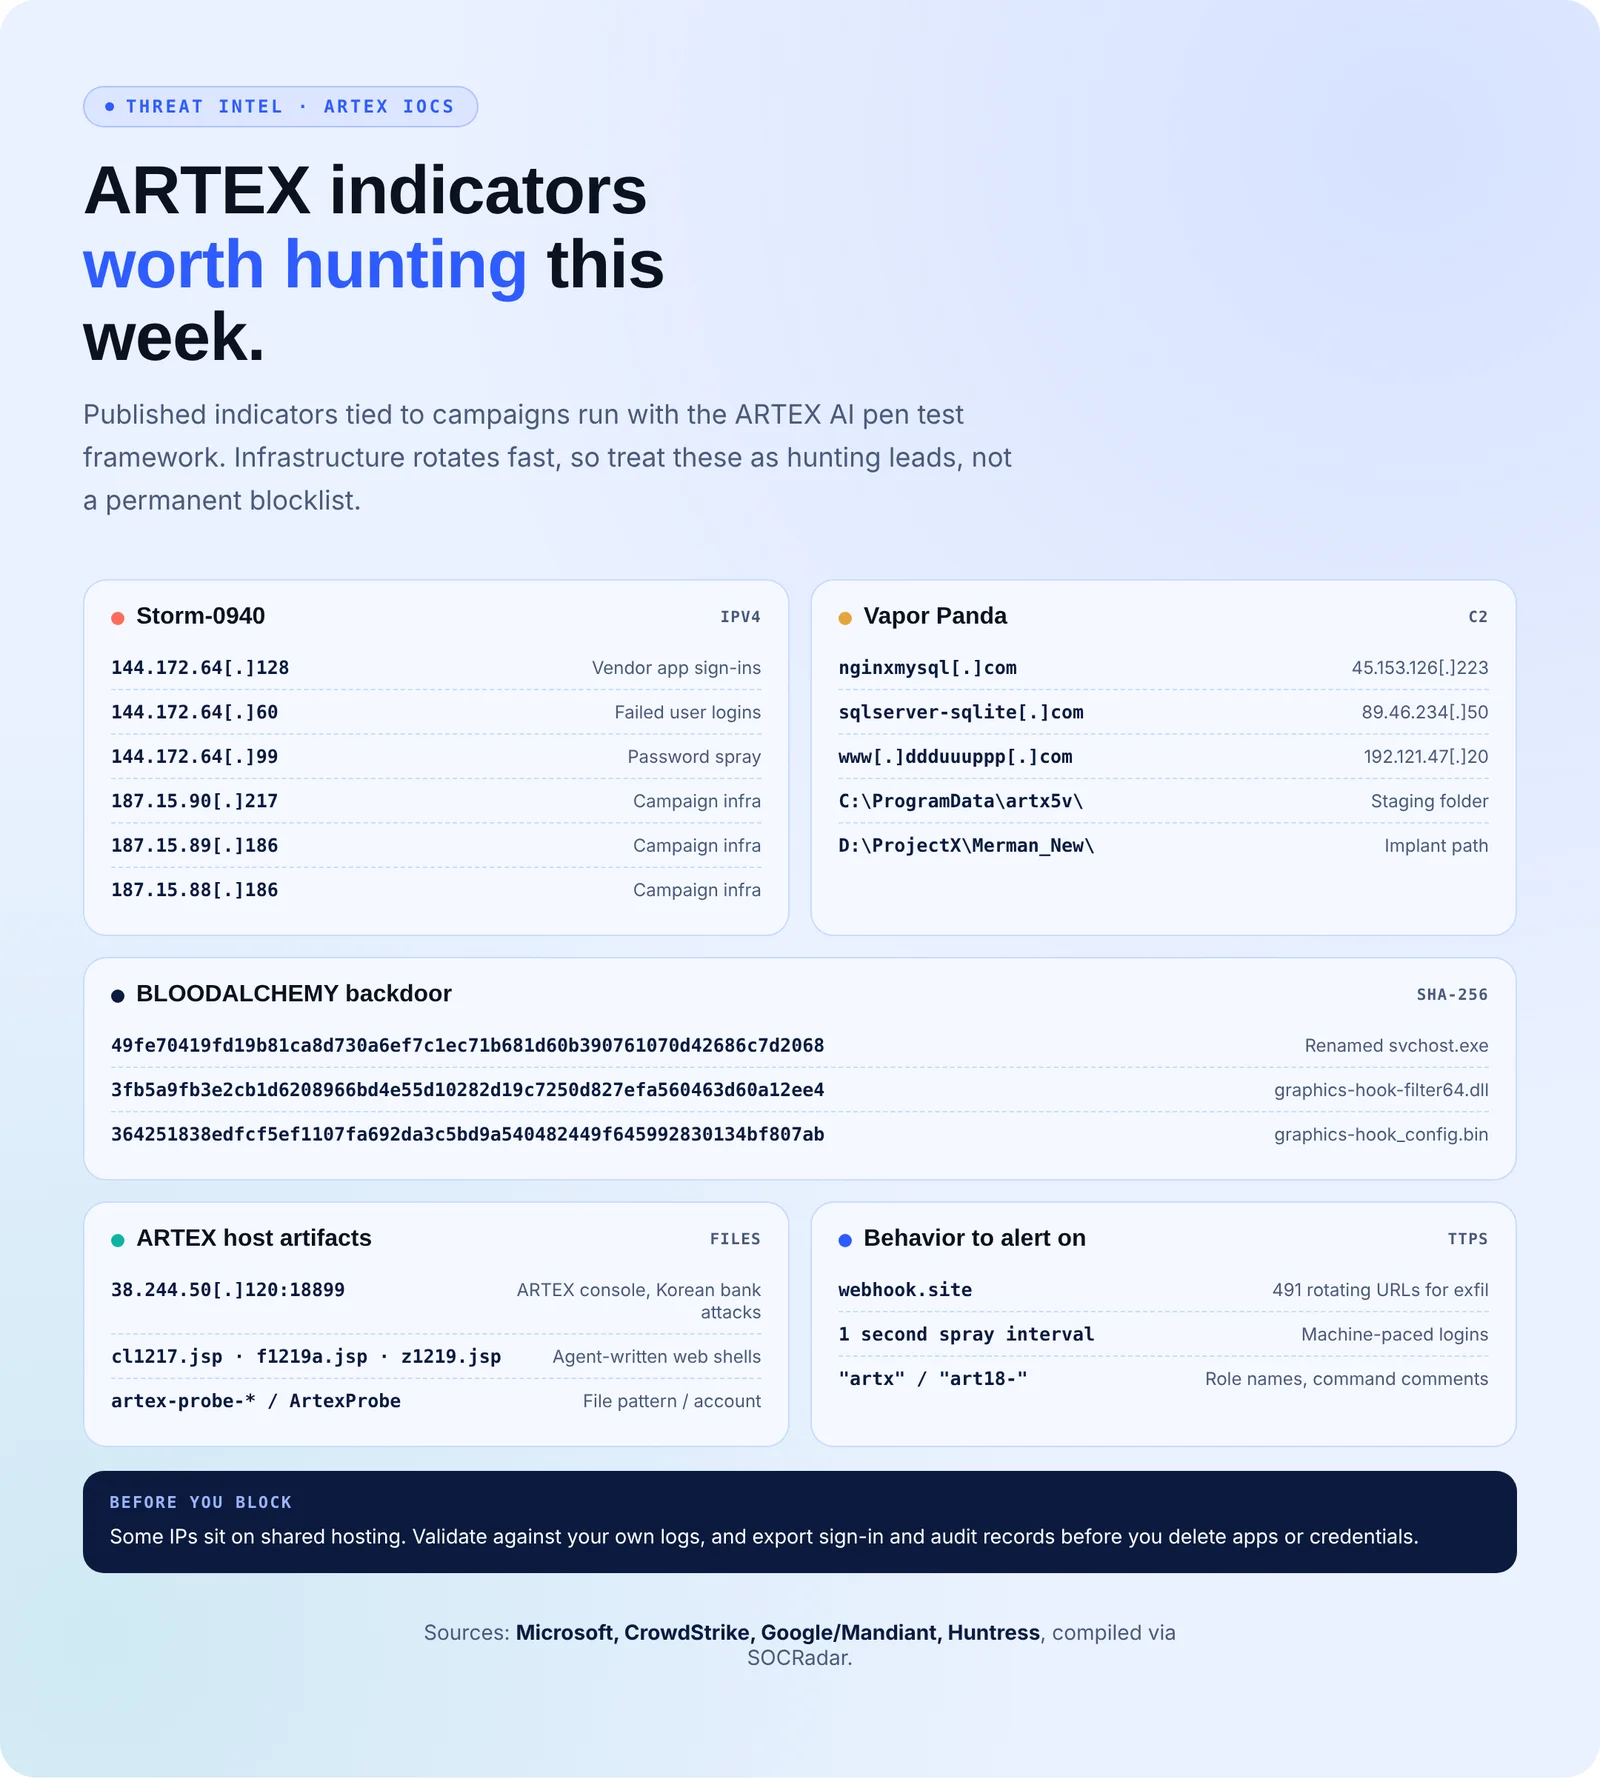
IOCs at a Glance
These indicators are tied to wider campaigns run with the ARTEX AI pen test tool, collected by SOCRadar from Microsoft, CrowdStrike, Google/Mandiant, and Huntress. Infrastructure rotates fast, so treat them as hunting leads. Validate before blocking, since some IPs sit on shared hosting.