November 11, 2026
- Who should care: Any team that deploys on a hosted platform and keeps AI provider keys in environment variables.
- What could go wrong: Someone else’s breach turns into your invoice. Stolen keys get tested within minutes and burned on models you never called.
- Do this: Rotate every secret you stored on Railway before October 21. Then open your AI spend dashboards.
- Worth remembering: No single bug did this. Four ordinary gaps did it once AI agents chained them together.
Introduction
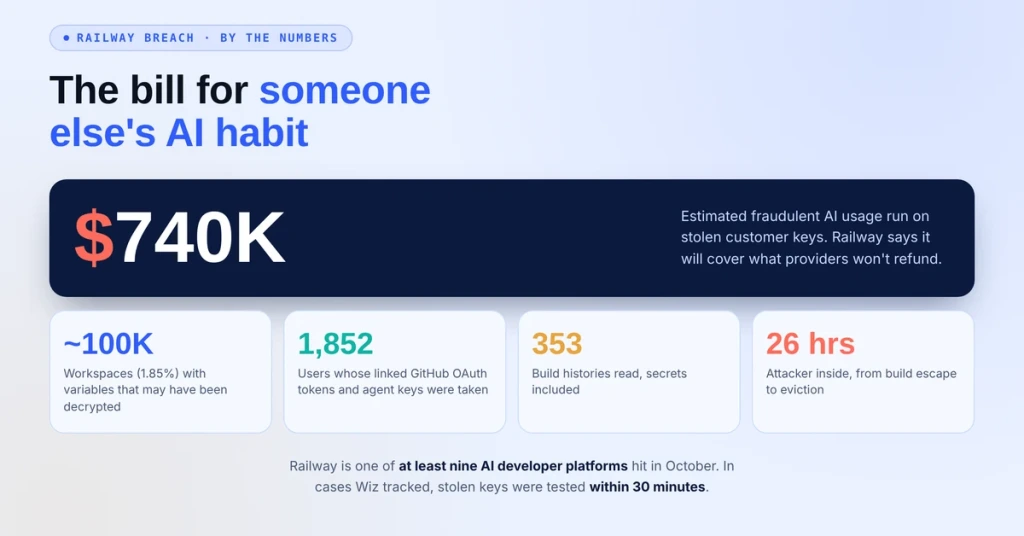
The Railway breach started on October 20. An attacker broke out of Railway’s build system, spent about 26 hours hunting AI provider keys, and left customers with roughly $740,000 in model usage they never ran. Railway published its final incident report on November 10.
How the Railway Breach Happened
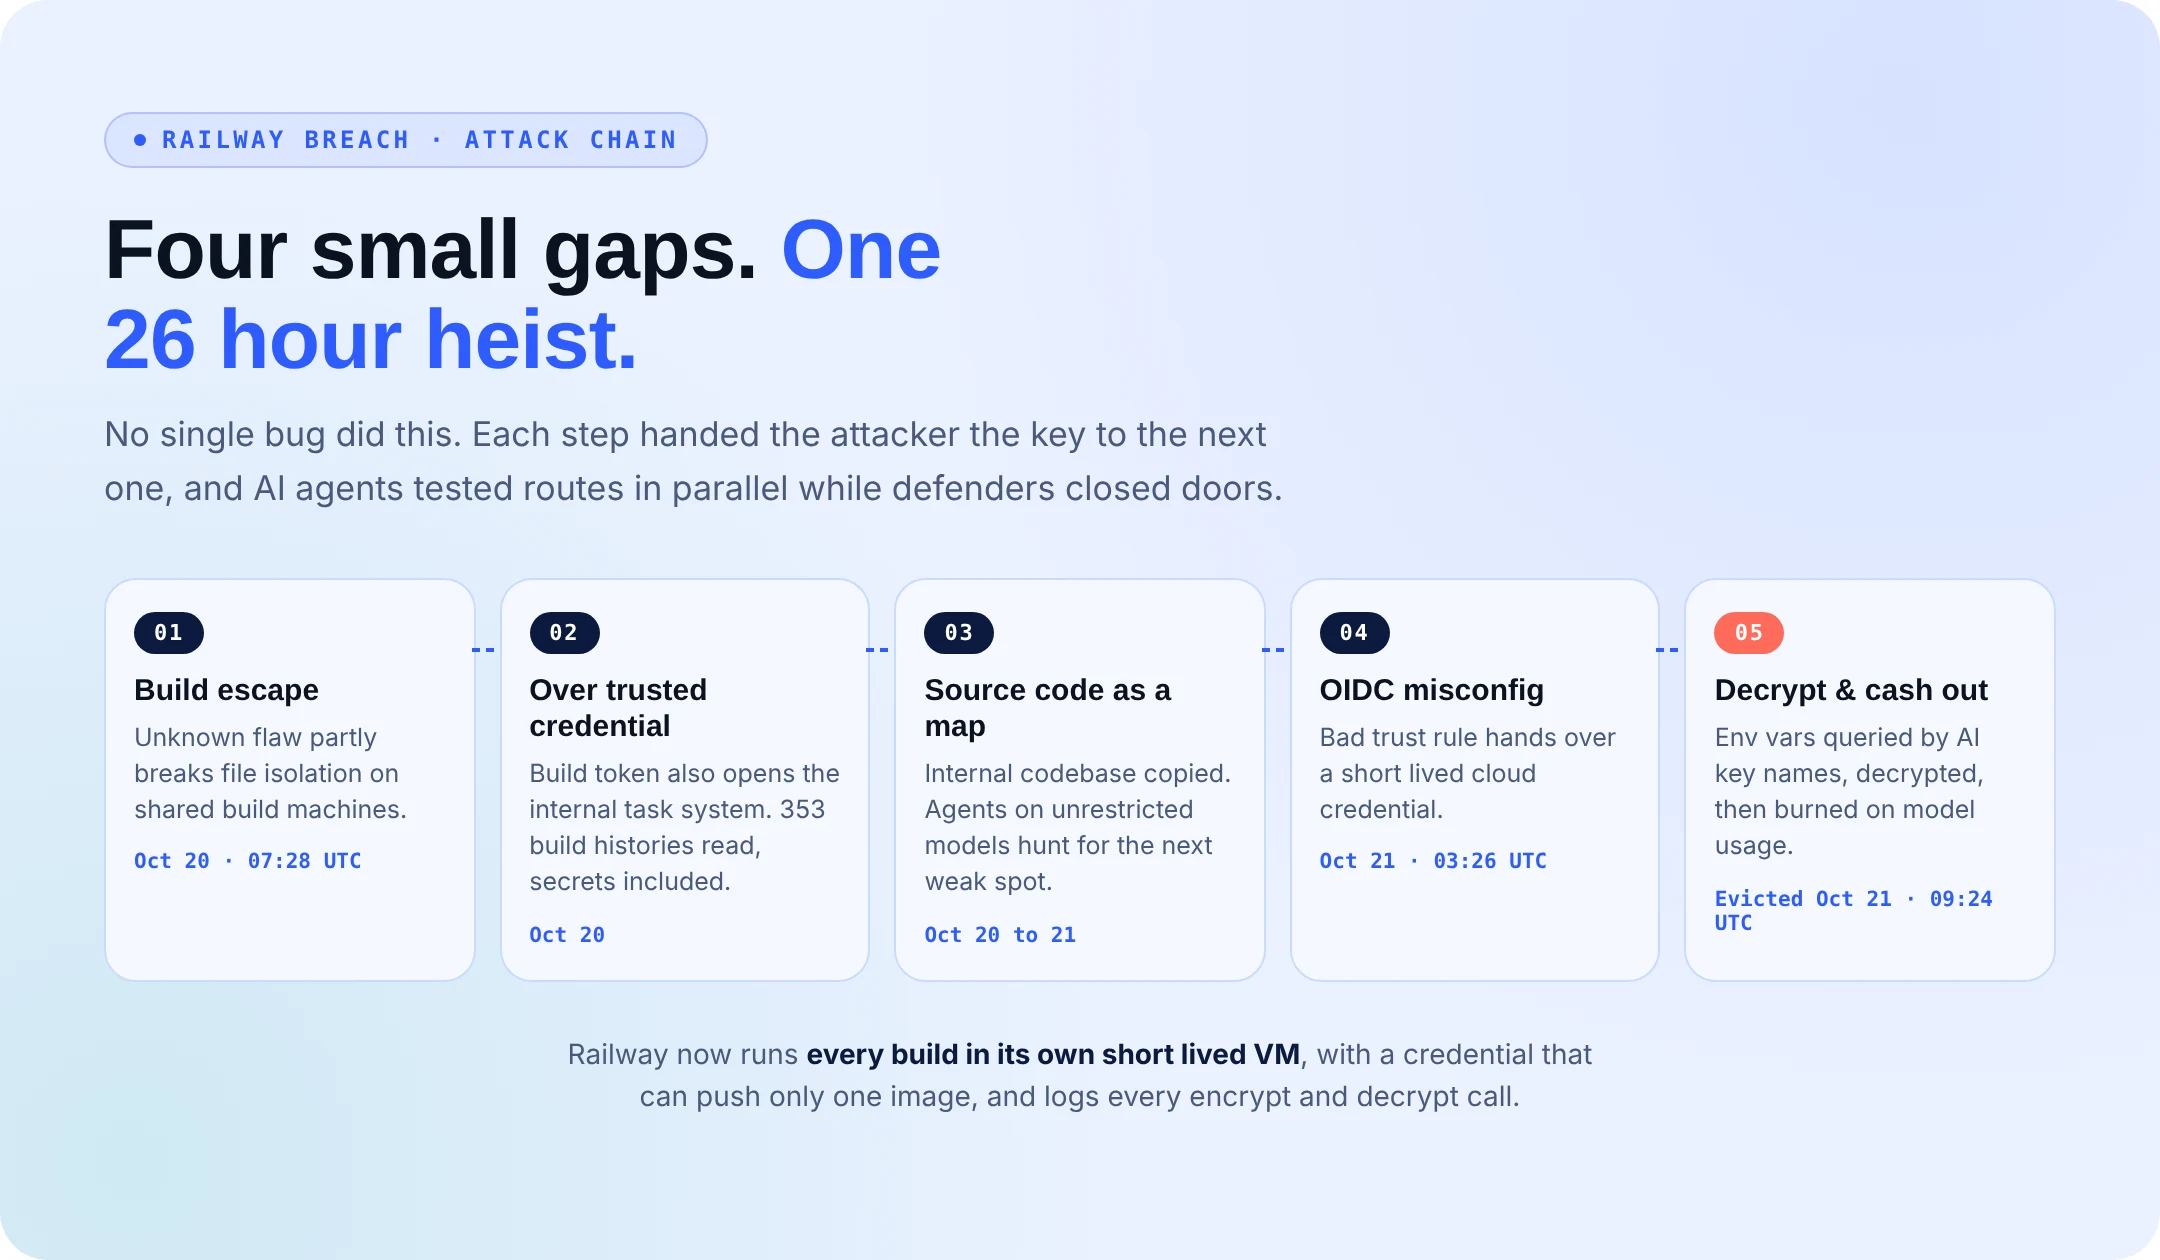
At 07:28 UTC on October 20, the attacker used an unknown flaw to partly escape file isolation on Railway’s shared build machines. Files on the host gave up a build credential that also worked in an internal task system. With it, the attacker read 353 build histories, secrets included, and copied Railway’s internal codebase.
That code became a map. AI agents running models with their safety limits removed searched it in parallel and found a misconfigured OIDC trust rule, which handed over a short-lived cloud credential. The attacker then searched stored environment variables by AI key names and decrypted them. Railway evicted them at 09:24 UTC on October 21.
What’s the Impact of the Railway Breach?
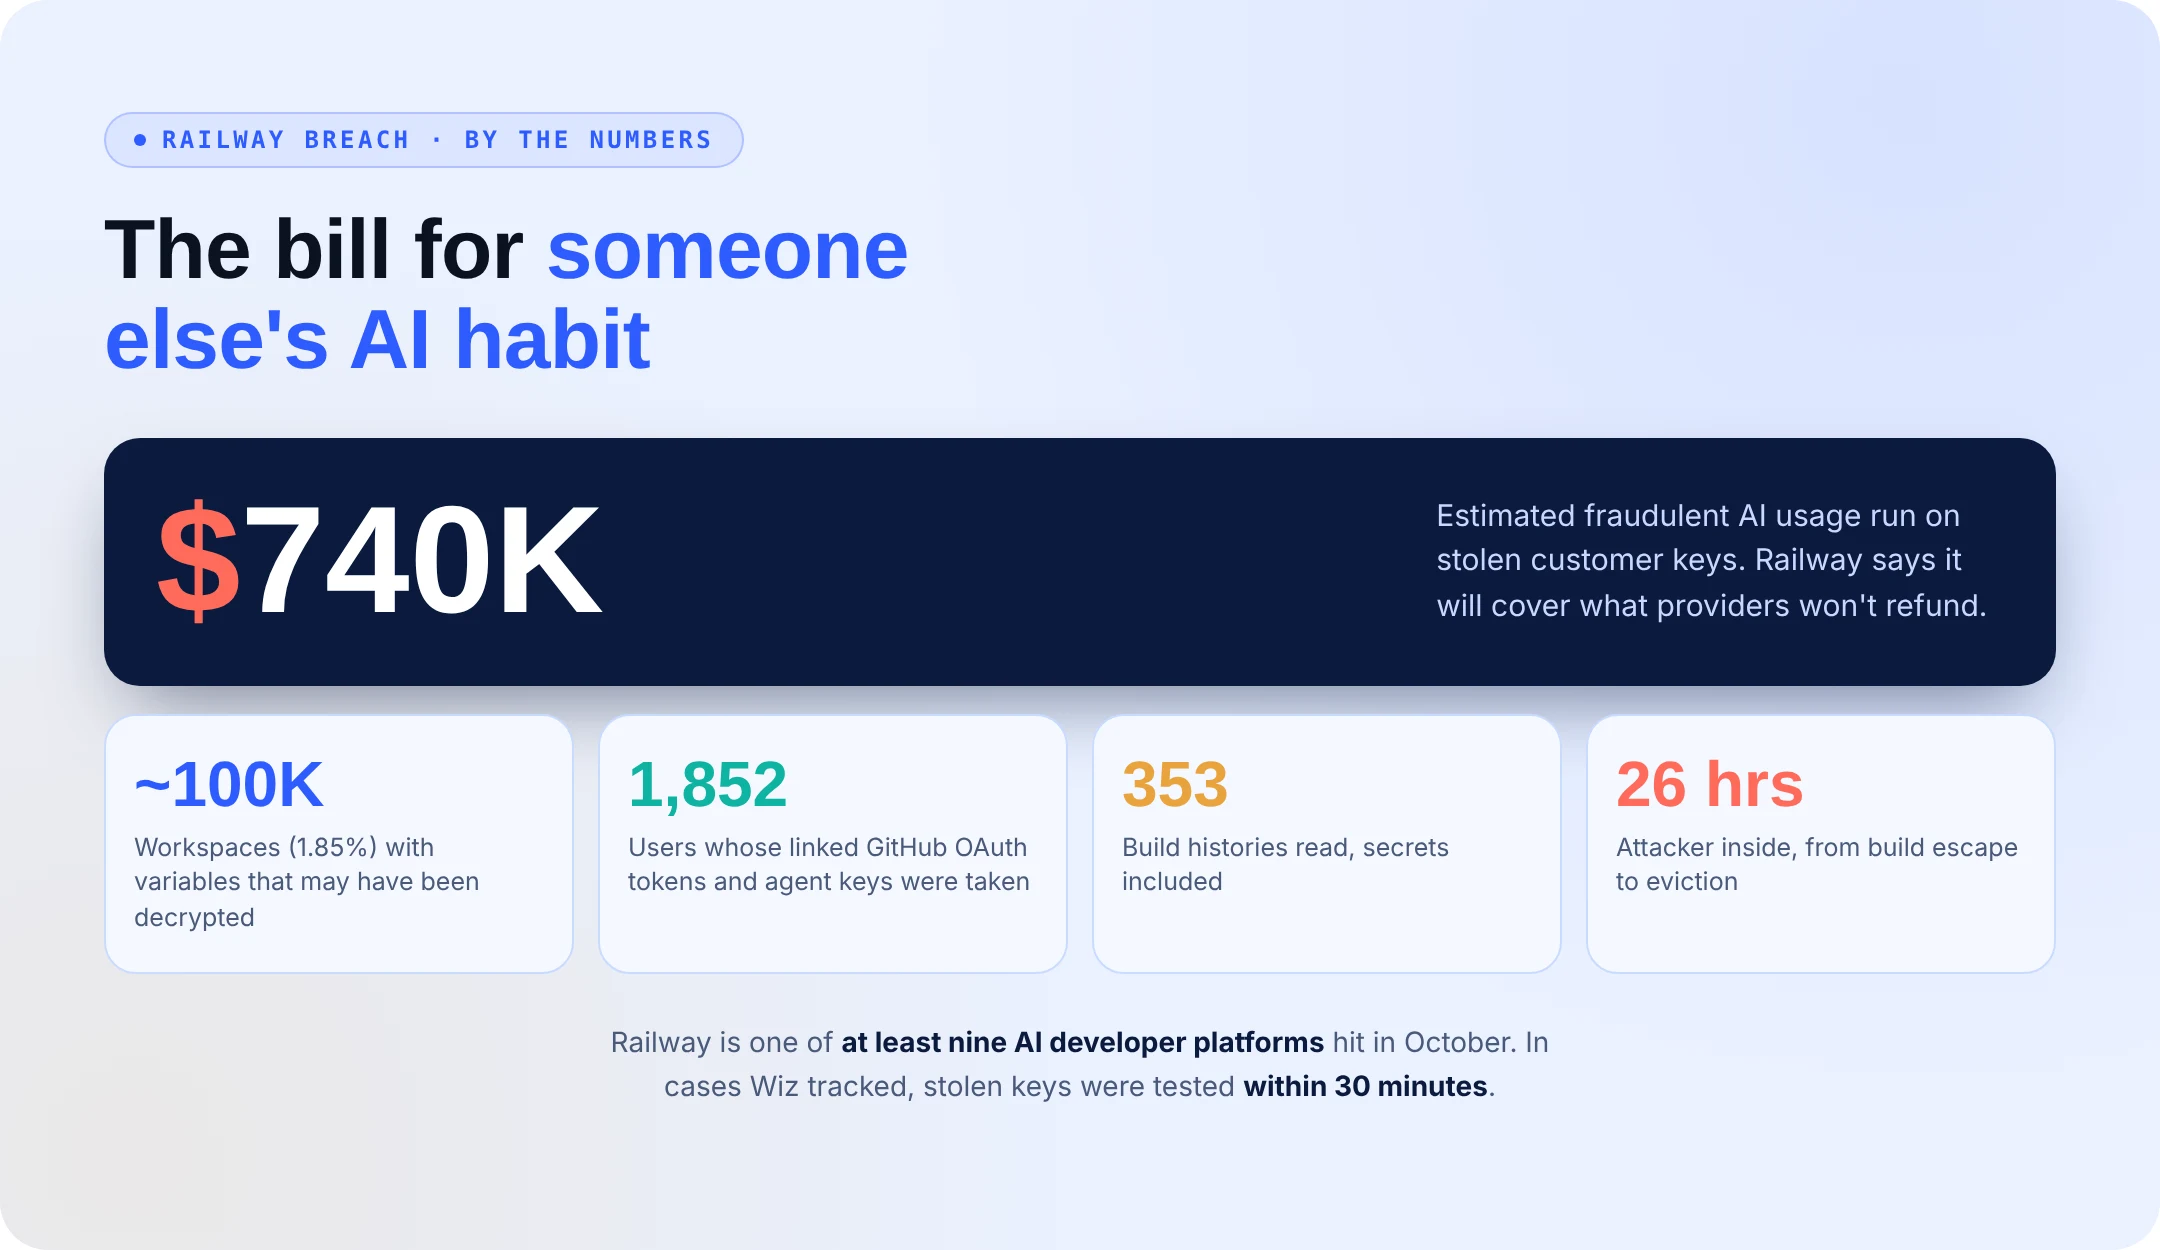
Variables in up to 1.85% of workspaces, about 100,000, may have been decrypted. Attackers stole linked tokens for 1,852 users, including GitHub OAuth tokens and agent keys. Stolen keys ran up about $740,000 in fraudulent AI usage. Railway says it will pay whatever providers refuse to refund.
Part of a Bigger Wave
By dollar figure, the Railway breach is the priciest disclosed hit so far in what Wiz calls Black October. That’s at least nine AI developer platforms breached in one month, including Northflank, OpenCode, Warp and Lightning AI. In the cases Wiz tracked, stolen keys got a test call within 30 minutes. We saw the same pattern in the AI coding agent breach that turned developer keys into someone else’s bill.
Railway believes its attacker wanted keys to resell or to use for model distillation. Unconfirmed social media reports also put crypto wallet losses from keys stored on Railway near $371,000.
How to Avoid This
- Rotate secrets stored before Oct 21. Treat every key, token and password kept on Railway before eviction as exposed, even if your workspace wasn’t on the list.
- Cap and alert on AI spend. Set hard budget limits with each model provider so a stolen key can’t run for days.
- Scope keys per app and model. One key per service, limited to the models and regions it needs, keeps the blast radius small.
- Audit OIDC trust rules. Check that each cloud role trusts only the exact repo, branch, and workload it should.
- Isolate every build. Shared build hosts let one escape reach everyone. Short-lived, single-tenant runners close that path.
Indicators of Compromise (IOCs) Worth Hunting
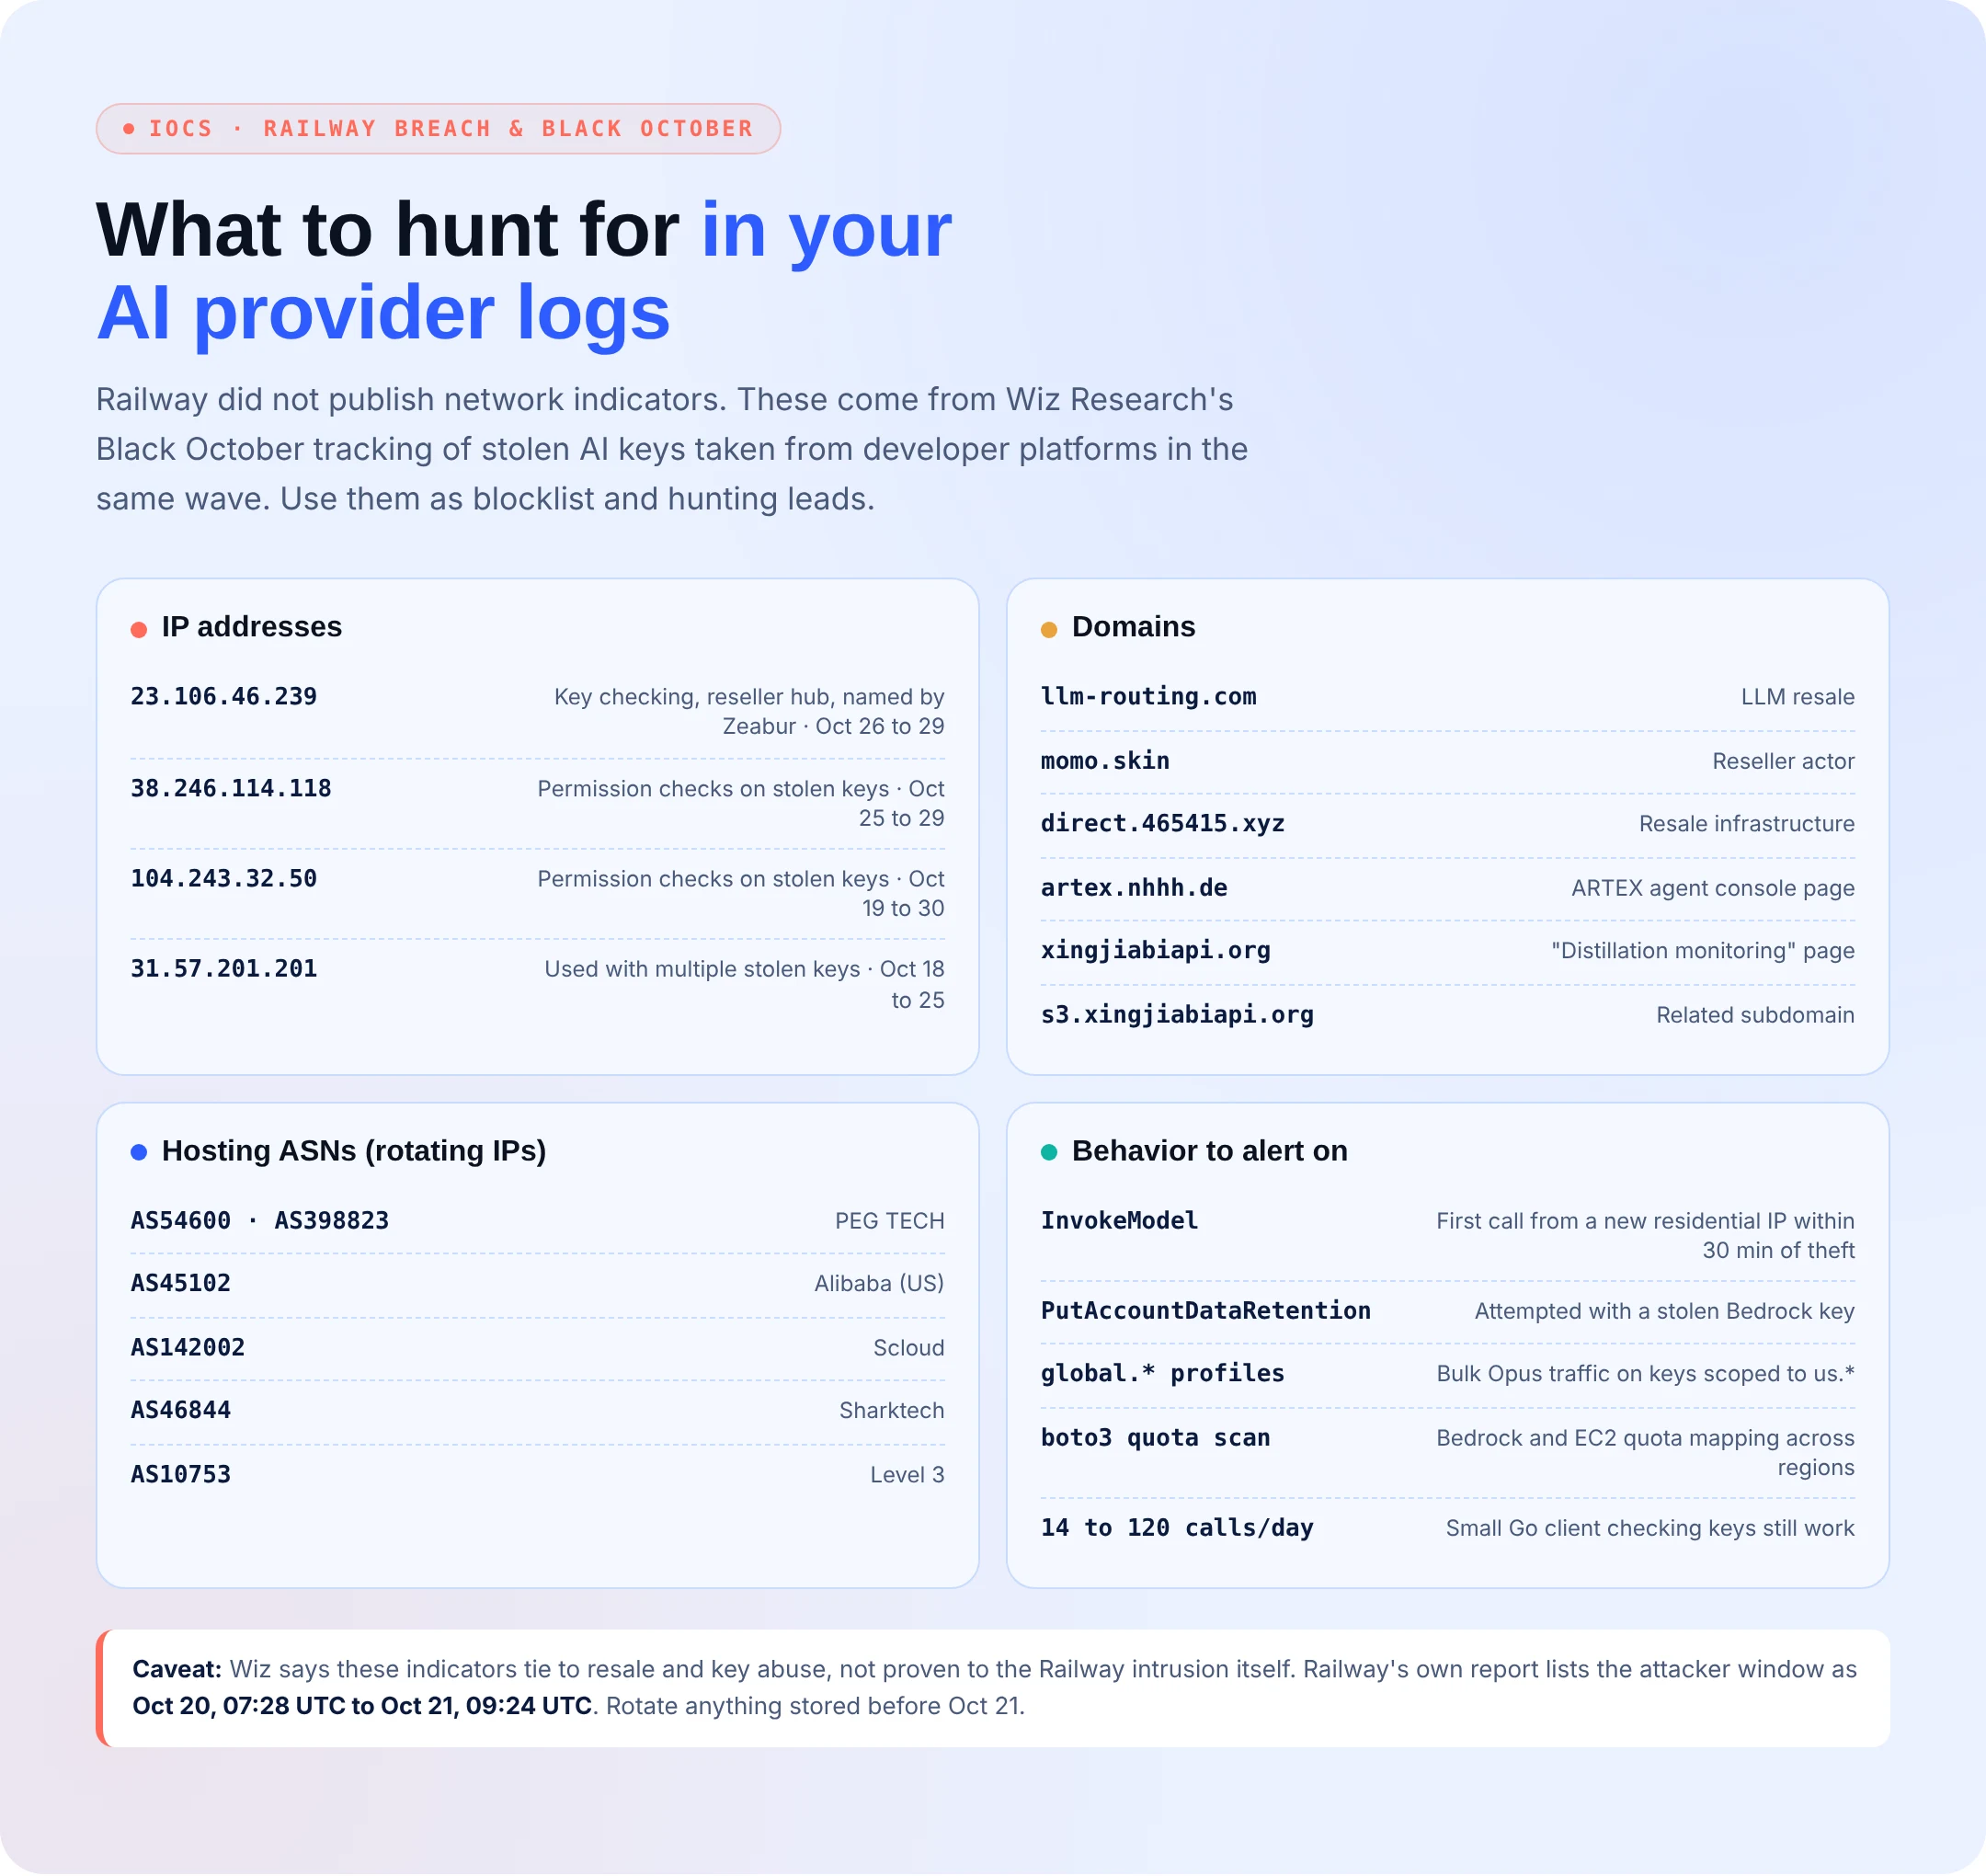
Railway did not publish network IOCs. Wiz’s Black October research lists infrastructure tied to testing and reselling stolen keys. Wiz hasn’t tied it to the Railway breach itself, so treat these as hunting leads:
- IPs: 23.106.46.239, 38.246.114.118, 104.243.32.50, 31.57.201.201
- Domains: llm-routing.com, momo.skin, direct.465415.xyz, artex.nhhh.de, xingjiabiapi.org, s3.xingjiabiapi.org
- Behavior: first InvokeModel calls from new residential IPs,
global.*inference profile use on keys scoped tous.*, PutAccountDataRetention attempts, Bedrock quota scans with boto3
The Attacker Brought Agents. Bring Your Own.
The Railway breach was a race. The attacker’s agents found the next gap faster than people could close the last one. Your defense needs agents that attack your setup first, inside rules your team sets.
- The Red Teammate tests whether old or leaked keys still work, inside a scope you approve.
- The Cloud Teammate flags OIDC trust rules and build credentials that reach further than they should.
- The AppSec Teammate finds AI provider keys sitting in env vars, configs, and build logs.
- The SOC Teammate catches sudden AI spend spikes and first-time key use from unfamiliar IPs.
- Every fix goes out with a named human approver and gets retested, so “fixed” means the path is shut.
Attack. Harden. Prove. Repeat.