Binance Warns iPhone Users as worse_query Code Hits GitHub
Binance issued an urgent warning Tuesday. A public iOS sandbox escape called worse_query can let a malicious app read files from other apps on the same iPhone. Seed phrases, private keys, and saved logins are all exposed.
- Who should care: Anyone holding crypto on an iPhone, and every security team that lets staff run wallets, authenticators, or work apps on iOS.
- What could go wrong: One bad app reads another app’s private files, seed phrases, and saved logins.
- Do this: Update to iOS 27.2.1 or 26.7.3 today and delete anything you sideloaded.
- Worth remembering: The exploit can’t drain a wallet by itself. You have to run the bad app first.
What Happened With the iOS Sandbox Escape?
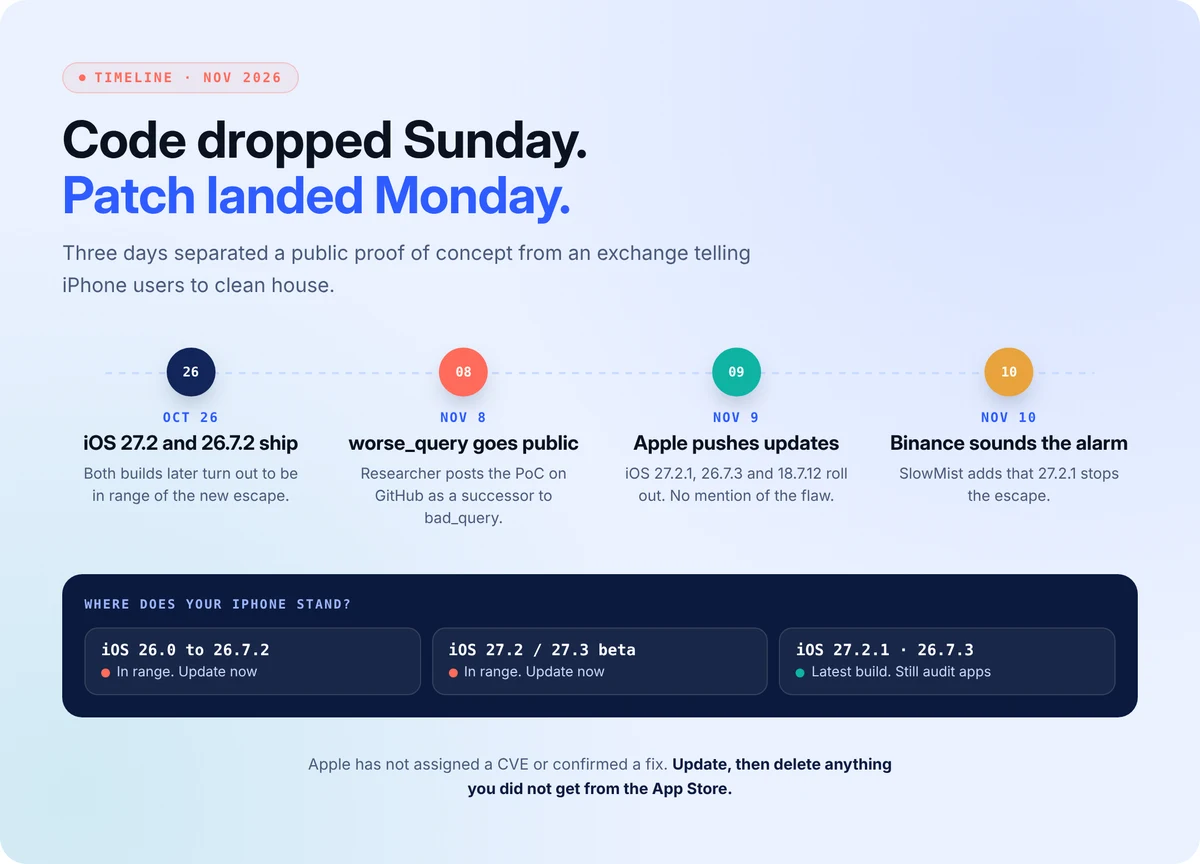
A researcher posted worse_query to GitHub on November 8 as a proof of concept for developers. It replaces an earlier escape, bad_query, and works on newer builds.
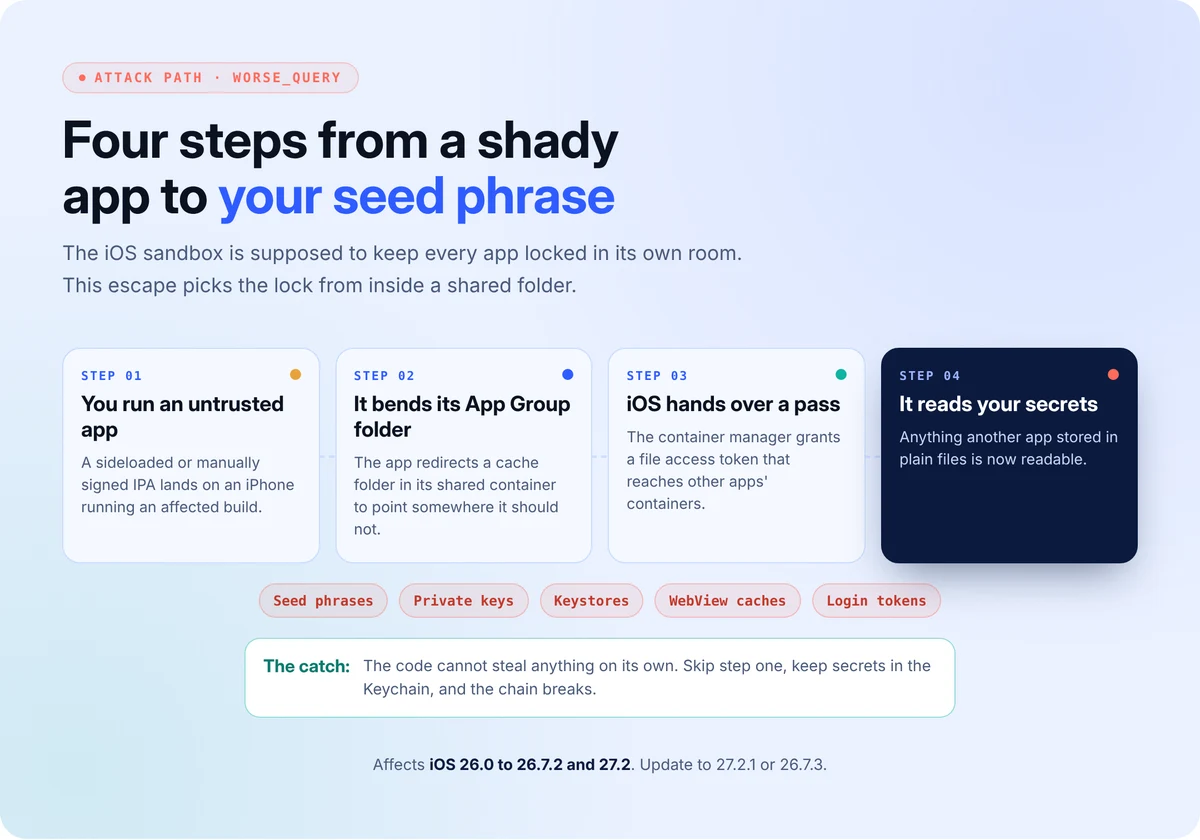
The app points a cache folder in its shared App Group container somewhere it shouldn’t, then gets the iOS container manager to hand over a file access token. With that token, it can read other apps’ data containers, shared group containers, and some iOS 27 system containers. The repo lists iOS 26.0 through 26.7.2 and 27.2 as affected. Binance’s alert names 26.7.1, 27.0.1, and 27.2.
Did Apple Fix the iOS Sandbox Escape?
Probably, but nobody has officially confirmed it. Apple shipped iOS 27.2.1 and 26.7.3 on November 9, one day after the code went public, plus 18.7.12 for older devices. Blockchain security firm SlowMist says 27.2.1 stops worse_query.
Apple’s release notes don’t mention the flaw, and it has no CVE yet. So install the update, but don’t assume it protects secrets that may already have been read.
What’s the Impact?
The sandbox is what keeps one app out of another app’s storage. An iOS sandbox escape breaks that wall, so any wallet keeping a mnemonic, keystore or WebView cache in plain files is readable. Session tokens for work apps sit in the same blast radius, so a personal phone problem becomes a company one.
This has happened before. In September, Binance flagged FomoPeek versions 1.1 and 1.2, an iOS app carrying code that broke out of the sandbox to grab keys. Back in February 2025, SlowMist tracked a fake app called BOM that hit more than 13,000 wallets and took over $1.82 million.
No theft tied to worse_query has been confirmed so far. With working code sitting on GitHub, though, that may not hold for long.
How to Avoid This
- Update to iOS 27.2.1, 26.7.3 or 18.7.12 now
- Delete sideloaded and manually signed apps
- Move funds to a new wallet set up on a clean device if a suspicious app ever ran
- Reset active sessions and rotate tokens on exchange and work accounts
- Wallet builders: keep keys in the Keychain, never in plain files
iOS Sandbox Escape Indicators of Compromise
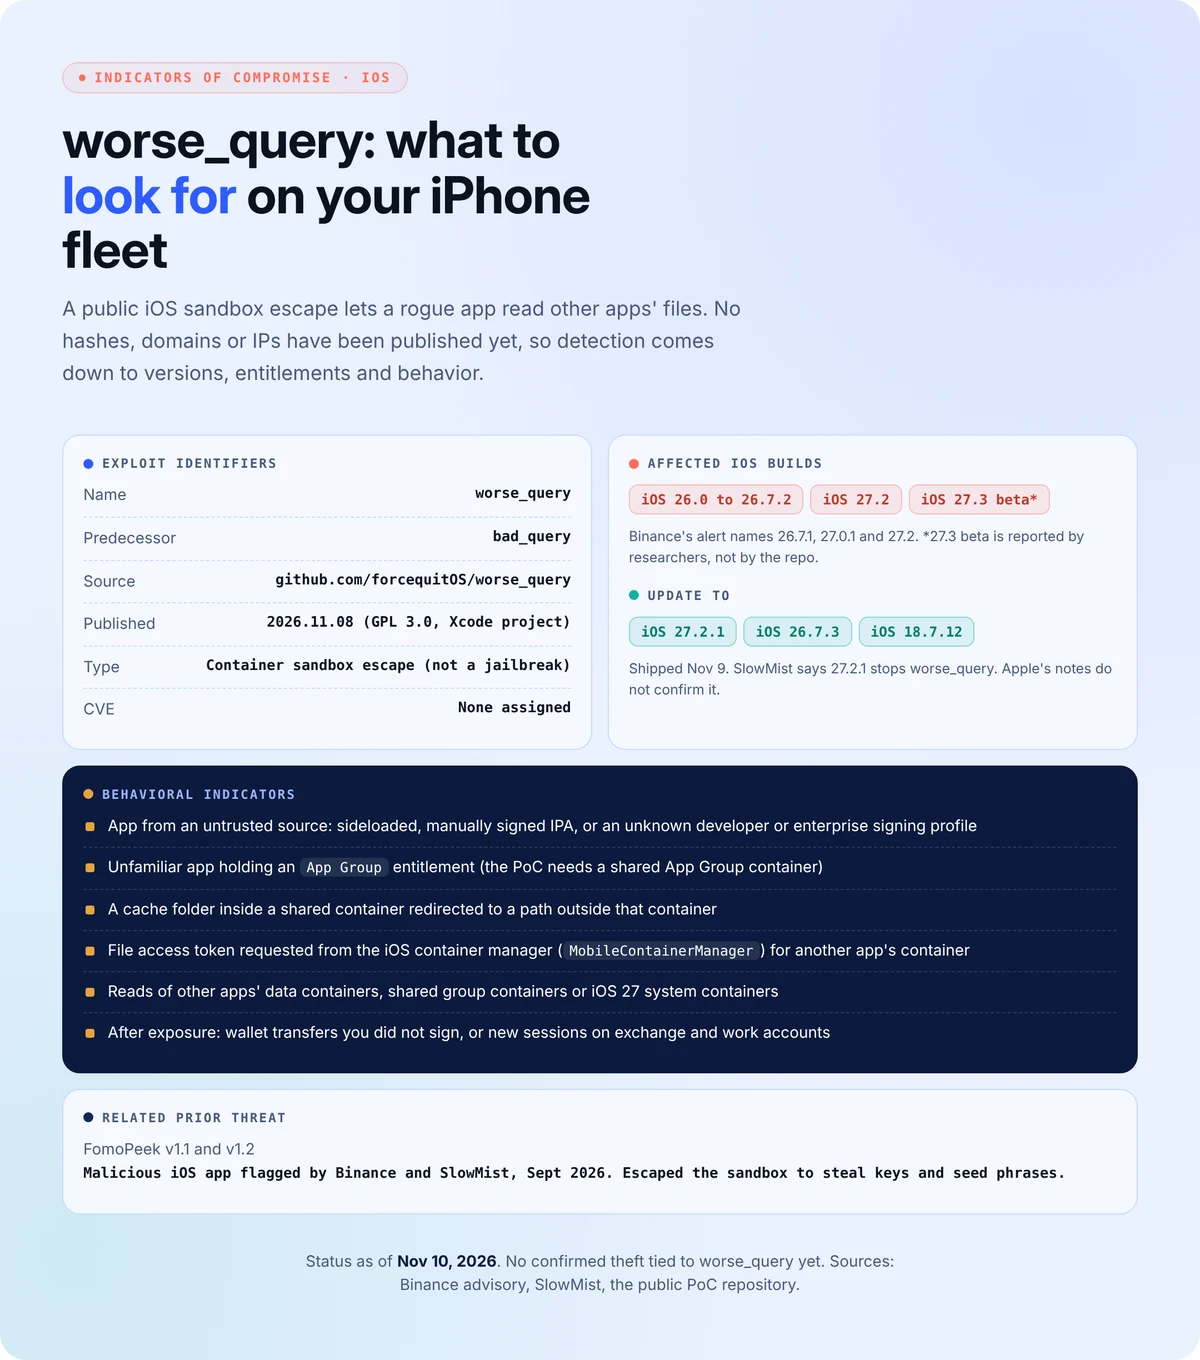
No hashes, domains or IPs have been published yet. Detection comes down to iOS versions, App Group entitlements and app behavior.
A Sandbox Is Only as Strong as Your Slowest Patch
A flaw like this hurts most on the phone nobody knew was still on iOS 27.2. Secure.com’s AI teammates find those gaps before an attacker does, and your team decides what to fix and when.
- Find every device on an affected build, unmanaged ones included
- Rank fixes by what each device can reach, so the finance lead’s phone goes first
- Gate every remediation behind approvals your team sets, with a full audit trail
- Retest after the update lands, so “patched” means proven
Governed Defense, Powered by Offense. Attack. Harden. Prove. Repeat.