Iris Ohyama Data Breach: No Cards Stolen, Plenty Still at Risk
SENDAI, JAPAN. One of Japan’s biggest household goods makers has learned an old lesson the hard way: your data is only as safe as the cloud service you park it in. The Iris Ohyama data breach started with one strange file in a vendor’s cloud and may have exposed 7.7 million shoppers.
Who should care: online retailers, anyone storing customer data with a third-party cloud provider, and every Iris Plaza shopper who reused a password.
What could go wrong: convincing phishing built on real names, addresses, and birth dates.
Do this: change any password you shared with Iris Plaza today.
Worth remembering: the breach hit a vendor’s cloud, not the storefront itself.
Introduction
Iris Plaza, the official online store of Iris Ohyama, says personal data tied to about 7.7 million people may have been viewed or stolen after an attacker got into an external cloud service the company relied on. As a result, the store has been offline since late October.
What Happened in the Iris Ohyama Data Breach?
On October 28, staff found a suspicious file sitting in a third-party cloud service used by the shop. The company pulled Iris Plaza and connected systems offline that same day, cut off the access route, and reported the incident to police and Japan’s Personal Information Protection Commission on October 29.
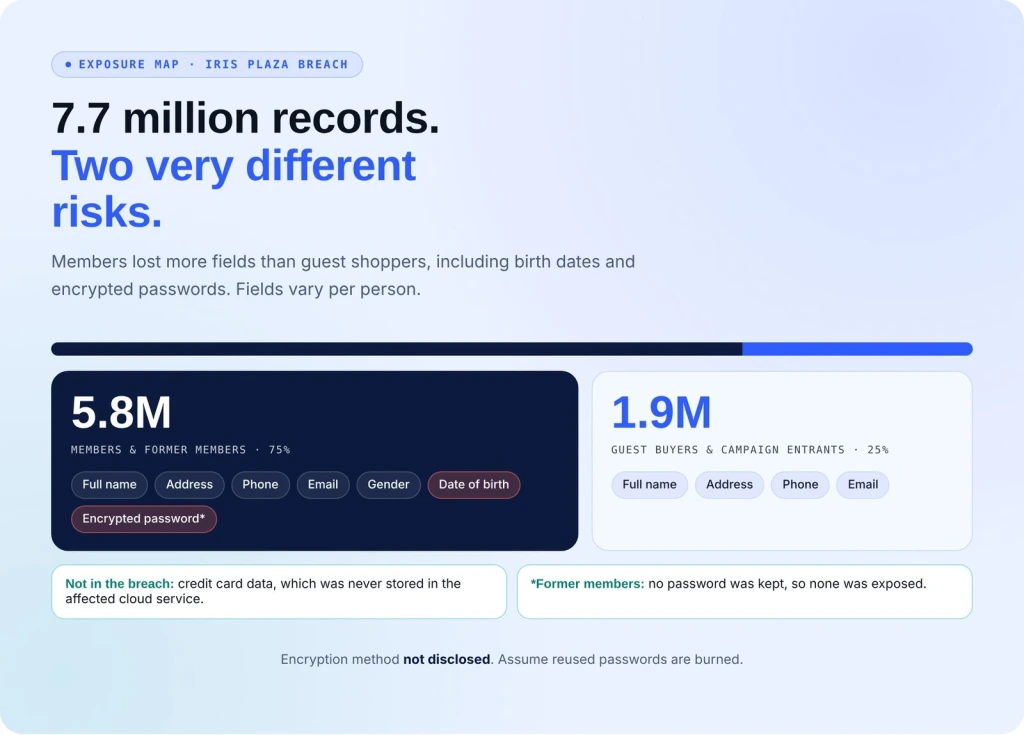
A second notice on November 5 put numbers on it. Roughly 5.8 million current and former members and 1.9 million non-members (guest buyers and campaign entrants) had data in the affected service. However, the company is still working out how many records actually leaked.
Members may have lost names, addresses, phone numbers, emails, gender, birth dates, and encrypted passwords. Non-members may have lost names, addresses, phone numbers, and emails. Former members, however, had no password stored. The company never kept card data in that service.
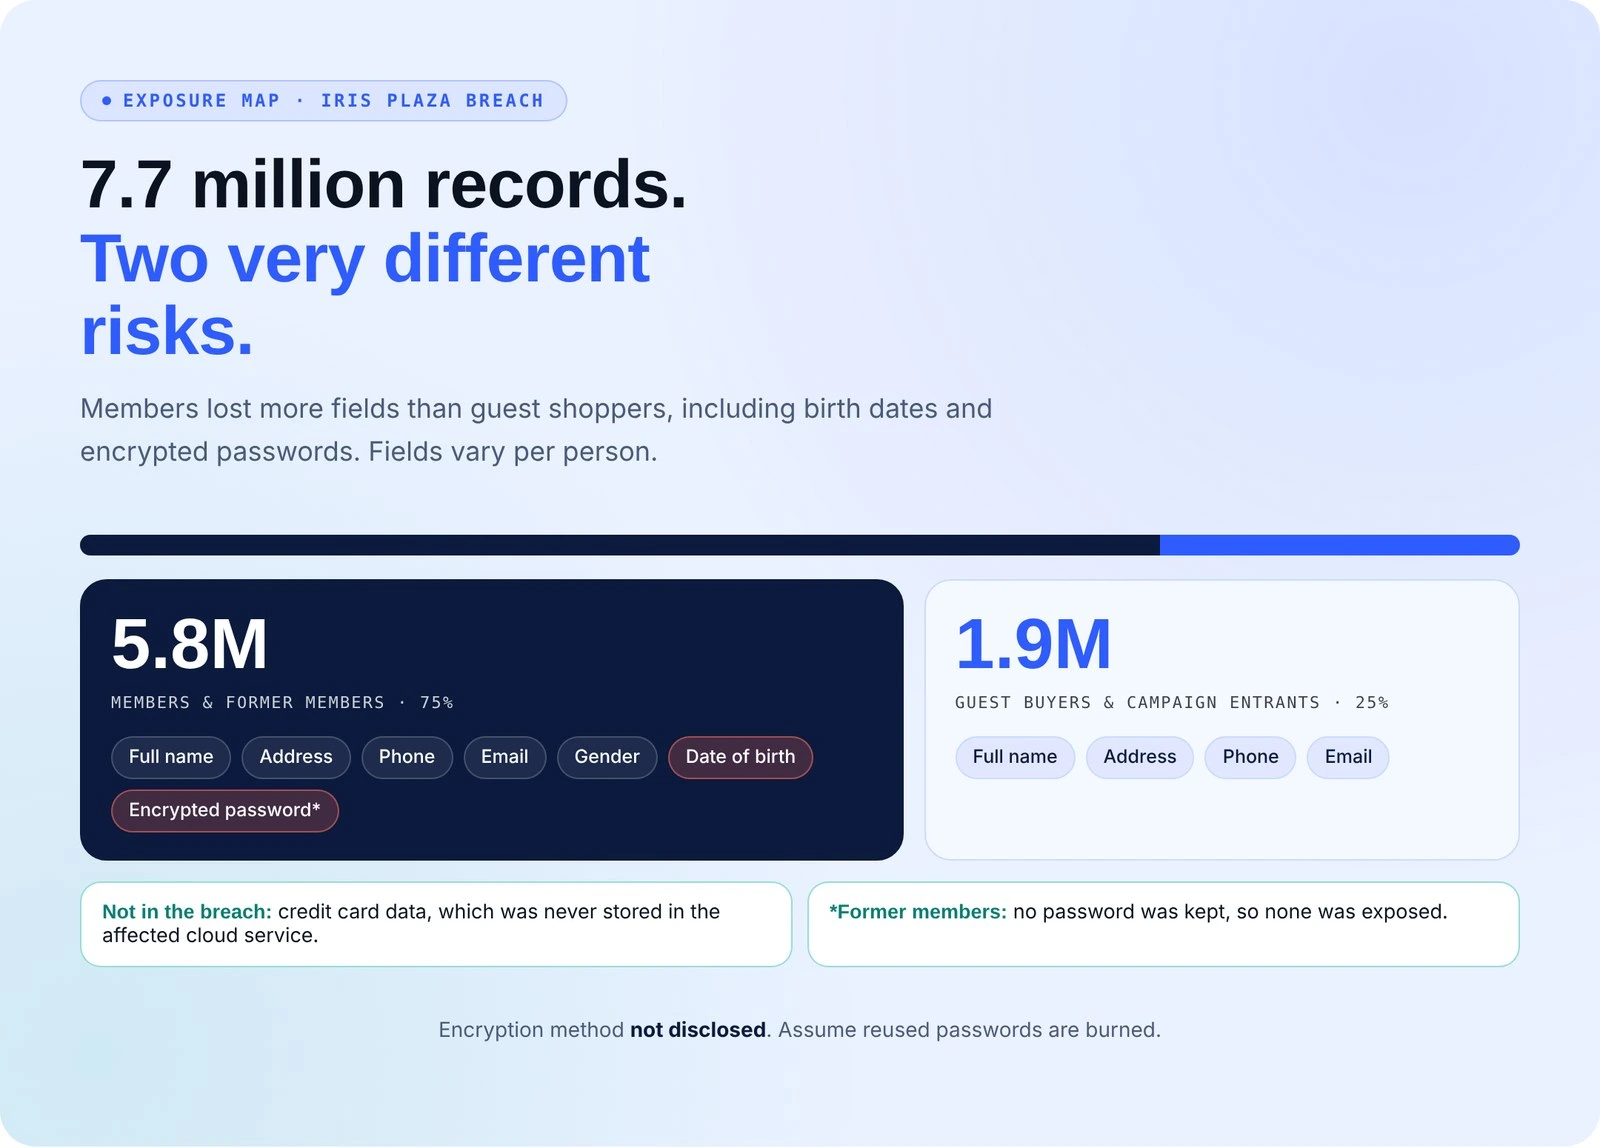
The company also paused the home fashion store SIMPLE STYLE and group appliance subscription and delivery sites as a precaution. Neither shows signs of a breach so far.
So far, the company has not named the cloud provider, the attacker, or the encryption method. A spokesperson told reporters the attackers have not contacted them.
What’s the Impact of the Iris Ohyama Data Breach?
For now, nobody has reported fraud. That’s the calm before the phishing wave. Real names, home addresses, and birth dates are a ready-made kit for fake refund texts, delivery scams, and account takeovers. And if those passwords were weakly protected, reused logins elsewhere are next.
Shoppers should also watch for look-alike storefronts. Iris Ohyama has warned before about fake Iris Plaza sites, and a breach like this gives scammers fresh bait.
How to Avoid This
- Map every third-party cloud store holding customer data
- Alert on unexpected files in cloud storage buckets, not only on logins
- Hash passwords with a slow, salted algorithm and say which one
- Purge data from former members on a fixed schedule
- Run phishing drills built around your own breach scenarios
Your Vendor’s Cloud Is Your Attack Surface
Iris Plaza found the problem because a file looked wrong. Most teams never look. The Iris Ohyama data breach reminds you that the gaps you miss end up in the news. Secure.com puts AI teammates on offense against your own defenses, so those gaps show up in your reports first.
- Continuously attacks cloud storage and SaaS configurations the way an intruder would
- Flags strange files, open buckets, and stale customer data as they appear
- Hardens what it finds within guardrails your team sets
- Proves every fix with evidence ready for regulators
- Hands analysts back hundreds of hours of manual cloud checks a month
Attack. Harden. Prove. Repeat.