
Fake Fines, Rigged RARs: How Gorbag Robs Ukraine’s Front Line Councils
A Russia-aligned spy crew has been stealing electronic signature keys, VPN configs, and saved passwords from Ukrainian courts, police, city councils, and defense firms since February 2025. The Gorbag BeautyStealer campaign grabs everything in one pass, then vanishes.
What Happened?
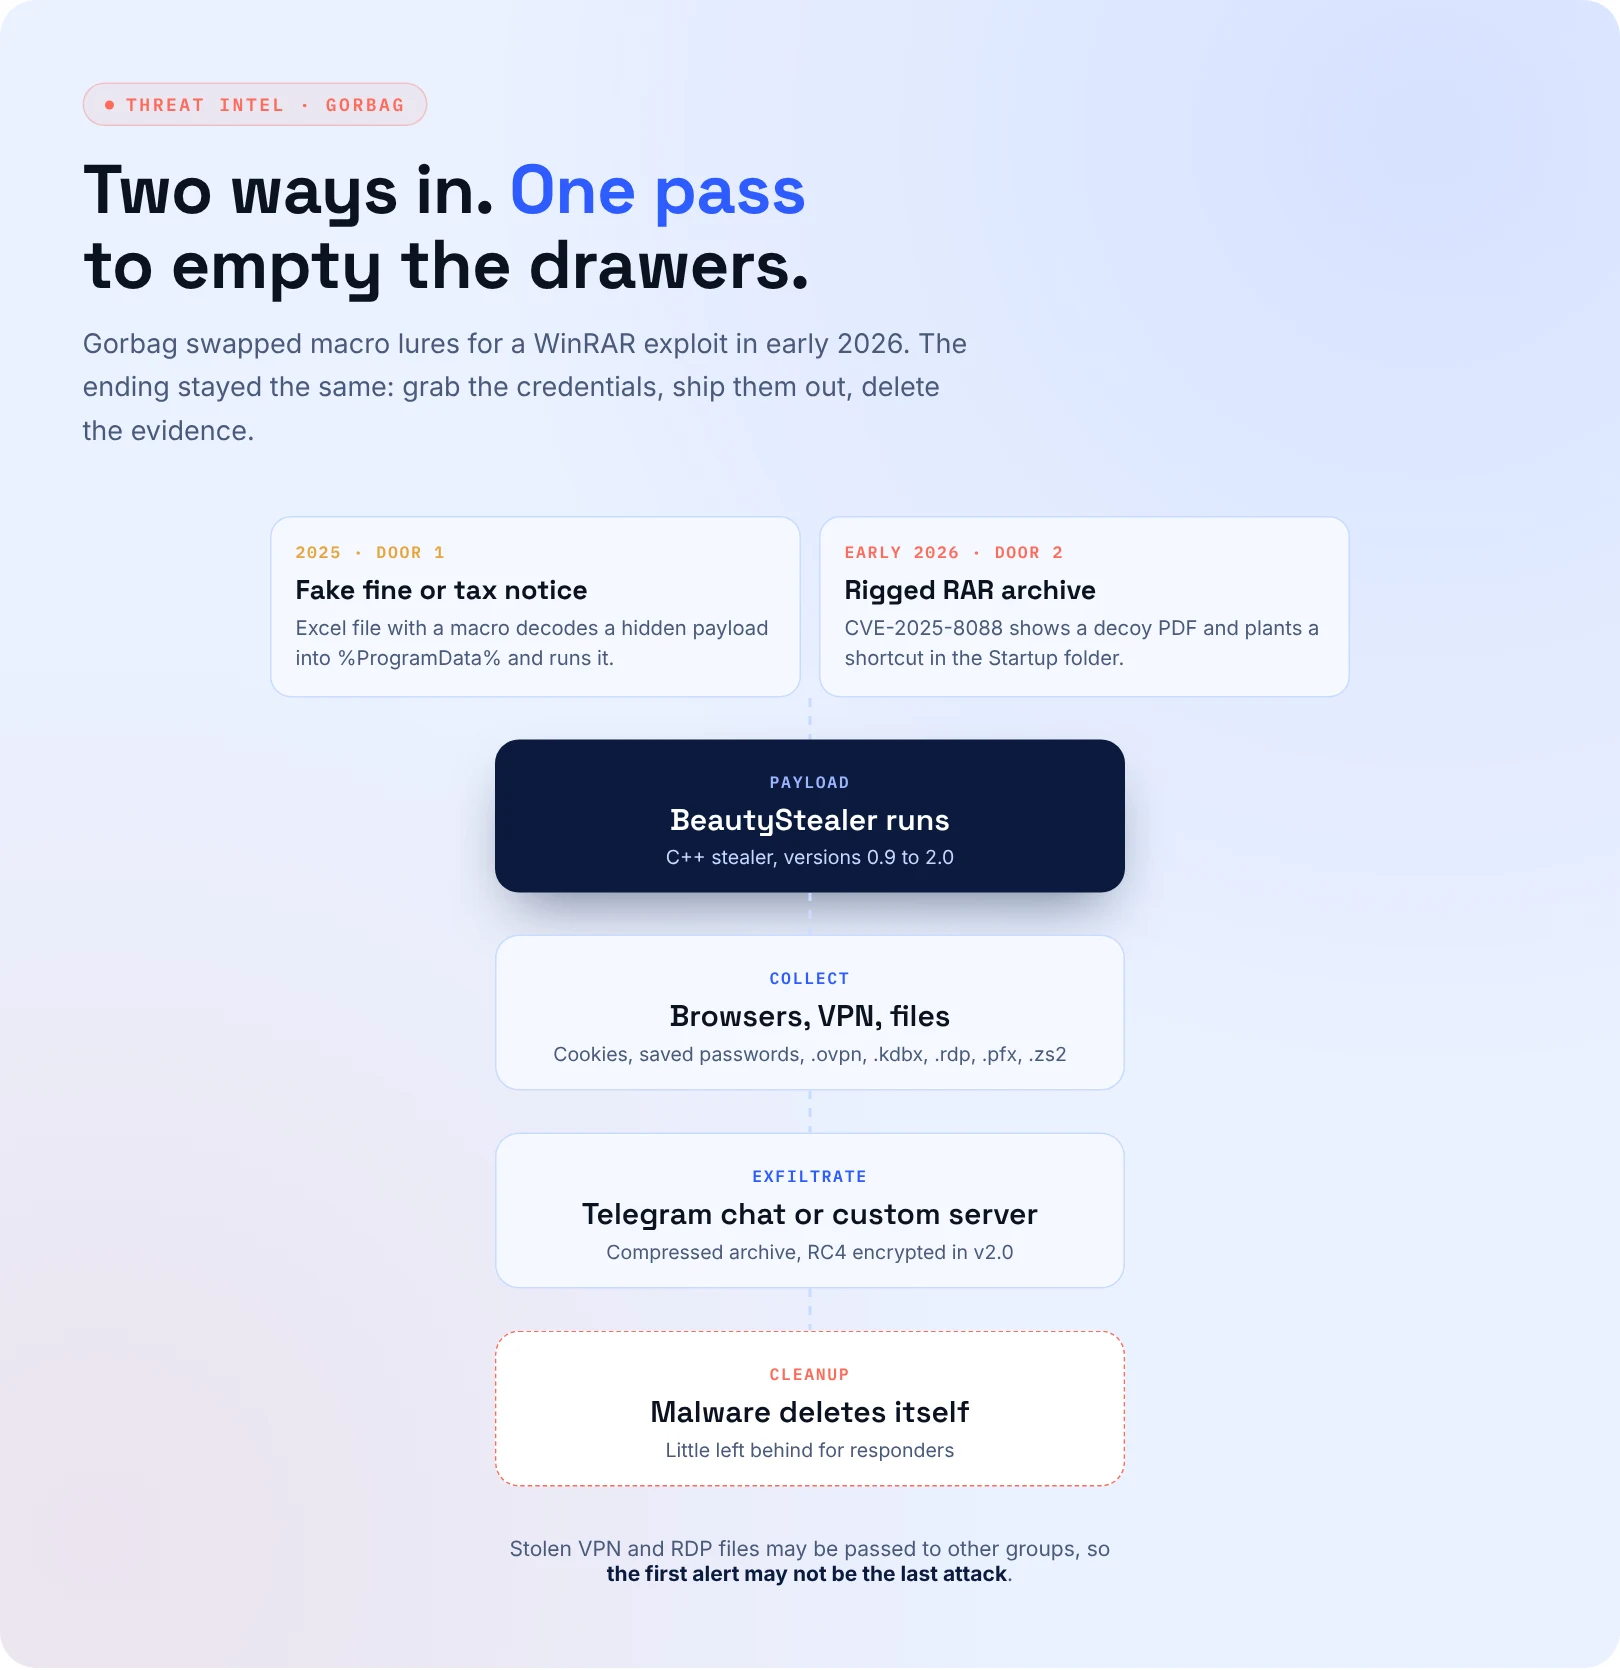
ESET published the research today, three weeks after presenting it at the Virus Bulletin conference. The group it calls Gorbag has hit only Ukrainian targets. Through 2025, victims got spearphishing emails about administrative fines or taxes. The emails carried an Excel file whose macro dropped BeautyStealer into %ProgramData%. One email came from a hijacked local government account.
In early 2026, the crew switched to rigged RAR archives that abuse CVE-2025-8088, a WinRAR path traversal bug that was already patched. Opening one shows a decoy PDF, while a shortcut lands in the Windows Startup folder.
Who’s on the Hit List
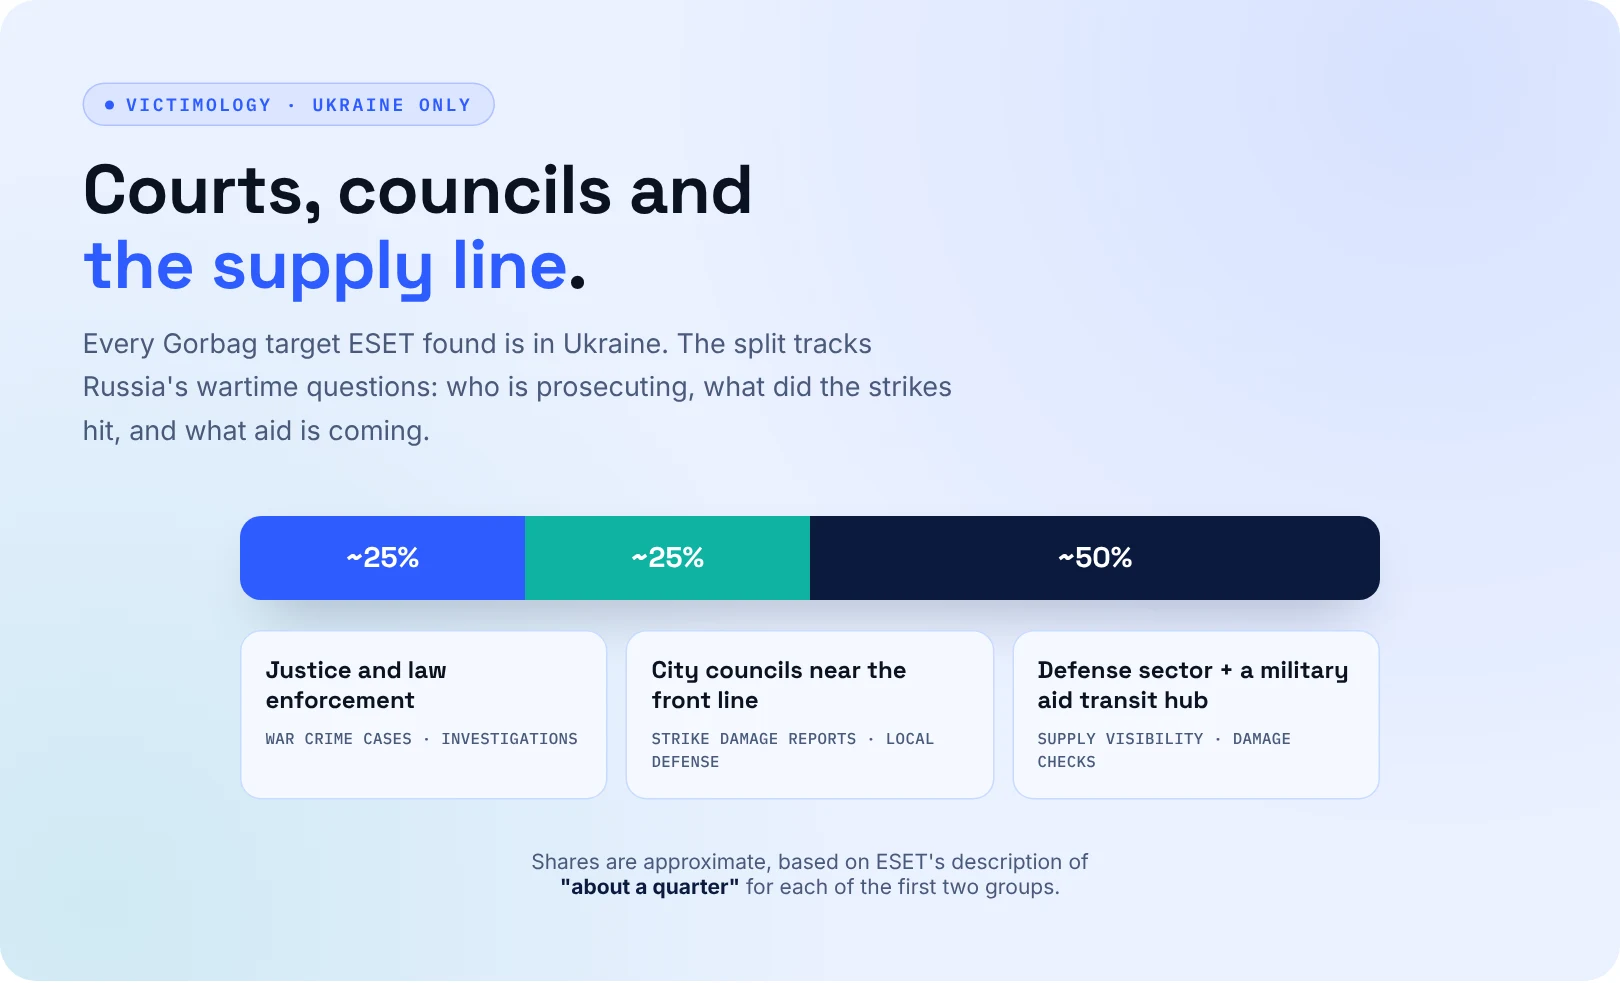
About 25% of victims are justice and law enforcement bodies, the people building war crime cases. Another 25% are city councils near the front line, and Russia has bombed almost all of those cities during the campaign. The rest are defense sector entities plus a major transit hub for foreign military aid. ESET suspects the council data helps Russia judge strike damage and the hub data tracks incoming aid.
What BeautyStealer Takes
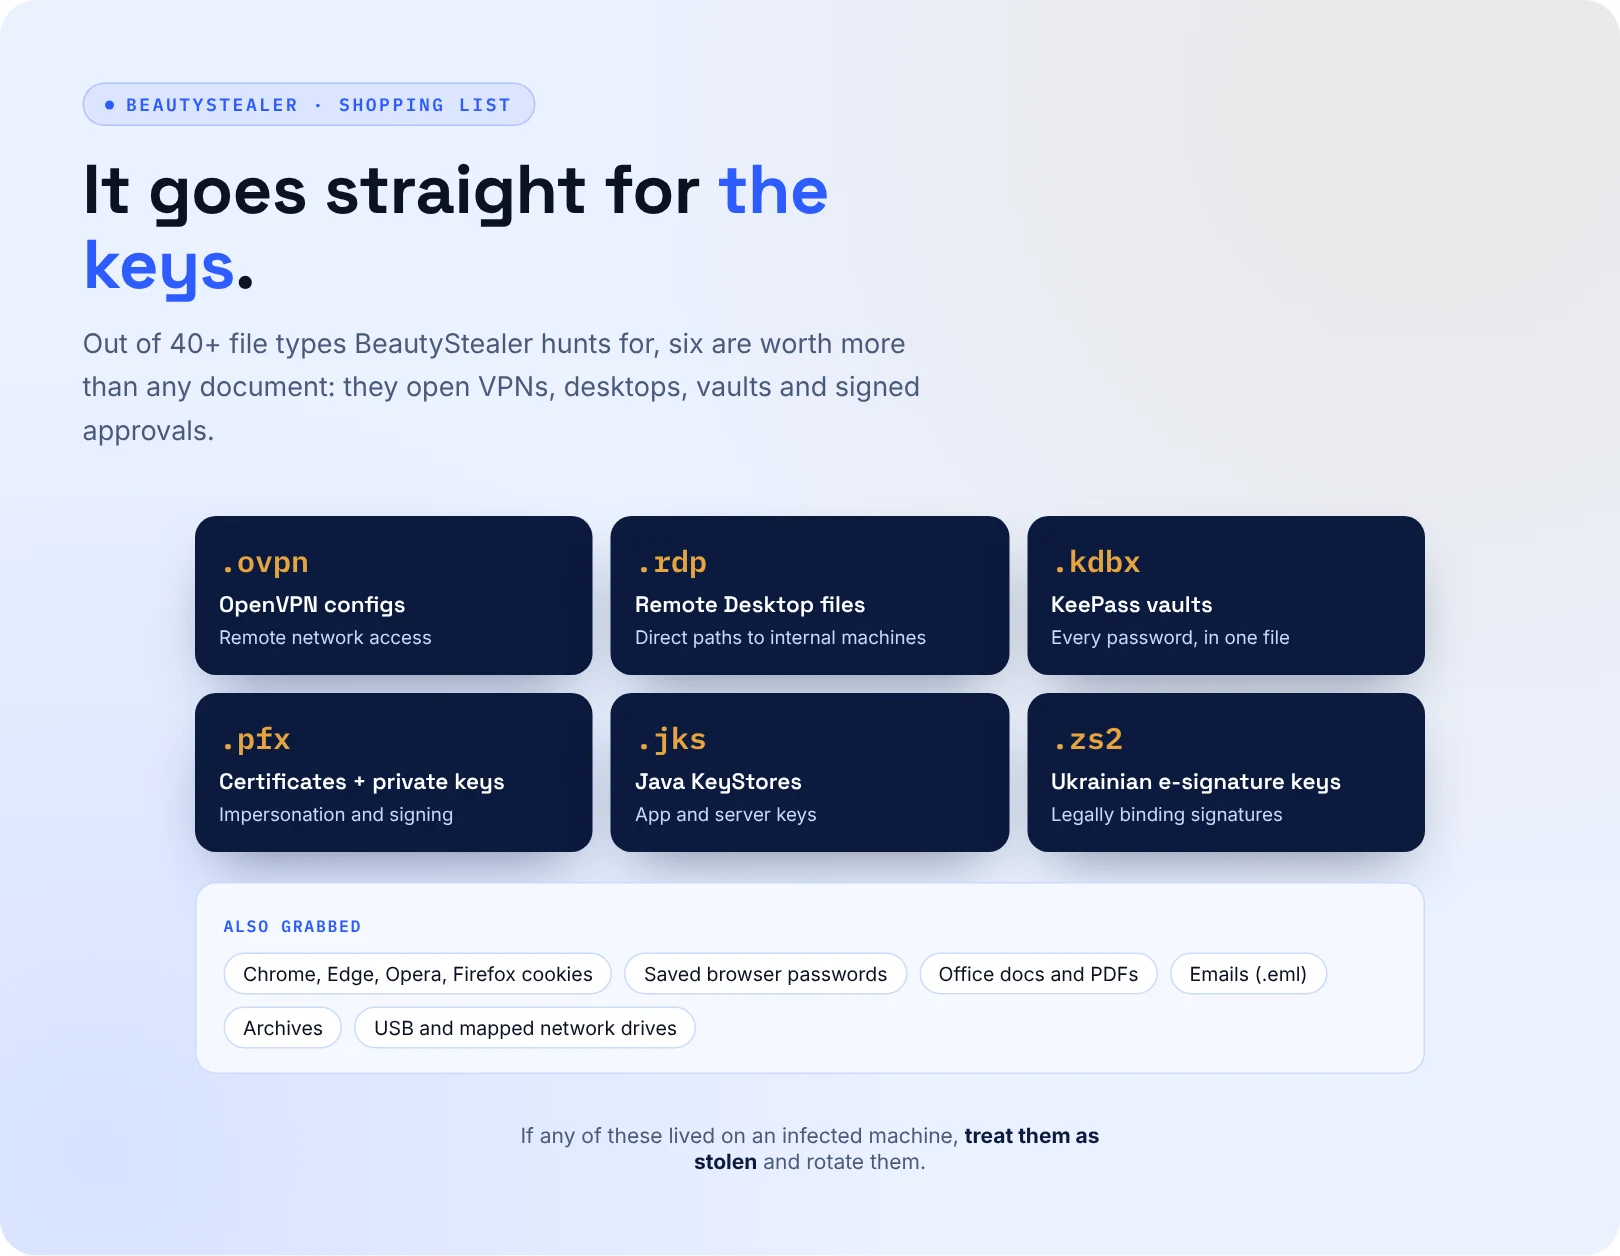
The C++ infostealer, tracked across versions 0.9 through 2.0, pulls cookies and saved passwords from Chrome, Edge, Opera and Firefox, plus OpenVPN configs. It also sweeps Desktop, Documents, Downloads, USB drives and mapped network shares.
It looks for Office files, emails, KeePass vaults (.kdbx), RDP files, .pfx certificates and .zs2 files, which hold Ukrainian electronic signature keys. The malware sends the loot to a Telegram chat or a custom server, then deletes itself.
It Tried to Fool the AI
An earlier tool, Prime ReverseShell, included a note telling AI reviewers the file was harmless prime-number code. ESET tested two AI assistants against it. Both called it a reverse shell anyway.
What’s the Impact?
VPN configs, RDP files, and session cookies let someone walk straight into a network. ESET thinks Gorbag may be an initial access broker that hands those credentials to other Russia-aligned groups. If so, the bigger break-ins could still be coming, and malware that deletes itself leaves responders very little to work with.
How to Avoid This
- Update WinRAR to 7.13 or later on every machine
- Block macros in Office files downloaded from the internet
- Treat “fine” or “tax” attachments as suspect, even from known government senders
- Alert on new shortcuts in the Startup folder and on scripts launching from %ProgramData%
- After any suspected infection, rotate VPN, RDP, and saved browser credentials and kill active sessions
Smash and Grab Only Works When Nobody’s Watching
BeautyStealer grabs its loot and deletes itself in a single run, which leaves almost no time to react. Secure.com can work around the clock, so lean teams get 24/7 coverage with no new hires, and a human approves every big move.
- Flags new Startup folder shortcuts and PowerShell running from odd paths, then opens a case with the context already attached
- Finds endpoints still running vulnerable WinRAR builds and sends the patch task to the right owner
- Spots logins from stolen VPN credentials or replayed cookies and asks a human before locking the account
- Turns published Gorbag IOCs into a hunt across your fleet the same day
- Logs every action so you can check what was done and why