TL;DR: A single poem on GitHub has quietly been running a botnet of more than 3,000 servers. It looks harmless. No links, no files, no code. But hidden in its lines is the address of the attacker’s control server, and the malware reads the poem to learn where to call home. Researchers are calling it the first adversarial poetry attack seen in the wild.
What Happened?
Threat researchers have tracked the cryptomining campaign since April. The malware, which they call PoeLLM, has hit more than 3,000 servers, mostly in the US and Western Europe. At its busiest, it took over more than 800 new servers in a single day.
It hunts for one thing: open source AI tools left exposed to the internet without patches. Most victims were running vulnerable versions of popular tools for serving and running AI models. Hundreds more were running an open-source document converter and a self-hosted code platform. Researchers believe the attacker also broke in through a known flaw in a commercial security appliance.
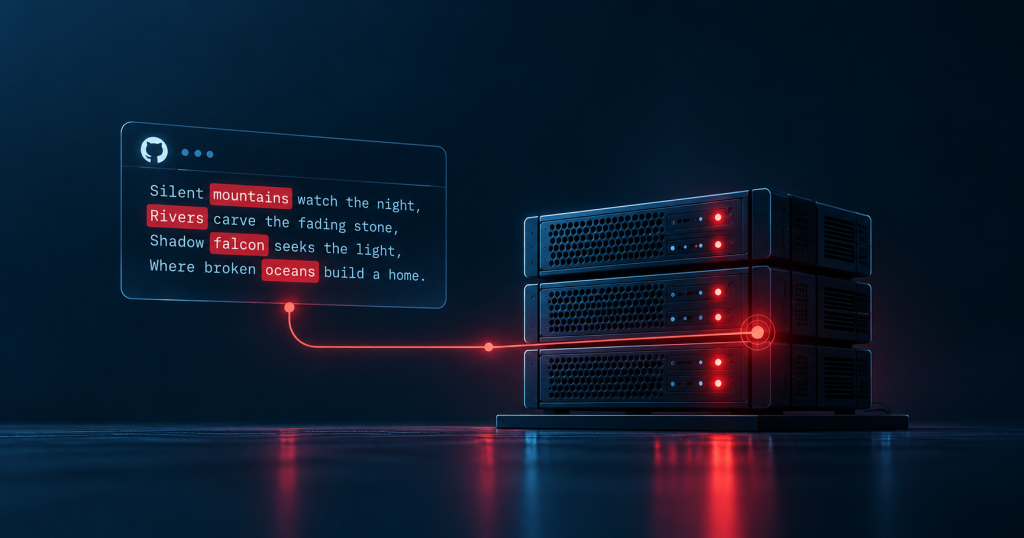
Here is the clever part. Instead of hiding its control server in encrypted traffic, it pulls the address out of a poem on GitHub. The poem has no links or code, so nothing for a scanner to flag. The malware reads set words from fixed spots in the poem and turns them into numbers that spell out the control server’s address. When the operator wants to move that server, they edit the poem, and every infected machine finds the new location.
What’s the Impact?
Once a server is taken, the malware does two jobs. It drops cryptominers that burn the victim’s expensive AI hardware to mine coins for the attacker. Then it turns the machine into a scanner and attack tool that hunts the next victim, which is how the botnet keeps growing on its own.
The bigger worry is the trend. Every new AI service a company spins up is another door, and security is often an afterthought in AI projects. For comparison, a separate supply chain attack on one AI tool this year reached about 2,500 companies. This campaign has already passed 3,000 victims, roughly 20% more, by going after several services at once.
IOCs (Indicators of Compromise)
PoeLLM / Canto Incognito: what to hunt for
Source and caveat: indicators are from the threat-intel team tracking this campaign and are current as of October 8, 2026. The control address rotates whenever the operator edits the poem, so treat the single IP as a starting point and pull the full, dated list from the researchers’ report.
How to Avoid This
How do you stay out of the net? Treat a self-hosted model server like any other internet-facing system, and keep every AI service patched. Pull admin and management pages off the public internet. Watch for the signs of a takeover: GPU usage that spikes for no reason, strange outbound traffic to mining pools, and your own servers suddenly scanning other machines. Lock down the commercial appliances on your edge and apply the vendor fix for the flaw being abused. And keep a live map of what AI services you have online, because you cannot defend what you do not know is there.
Your AI Stack Grew Overnight. So Did Your Attack Surface.
Teams are shipping AI services faster than they can secure them, and attackers are counting on it. The exposed, unpatched model server you forgot about is exactly the door this campaign walks through.
- A Red Teammate scans your perimeter the way this attacker does, finding exposed and unpatched AI services before a botnet does.
- A Cloud and Infrastructure Teammate flags the risky setup, like an admin page left open or a model server missing a patch.
- A SOC Teammate catches the takeover early, from odd GPU spikes to your own boxes scanning the internet.
- Attack findings turn straight into hardening work, so gaps get closed instead of filed away.
- Every consequential move waits for your team’s approval and lands in a full audit trail, so people stay in control.