Key Takeaways
- SAMA CSF Level 3 is the mandatory minimum for every SAMA-regulated fintech, and it requires documented, board-approved, and actively monitored controls, not just policy on paper.
- A realistic timeline for a startup beginning at Level 0 or Level 1 is nine to eighteen months, with eighteen months being the more common real-world outcome.
- The roadmap runs through six phases: gap assessment, governance foundations, control build-out, monitoring maturity, independent testing, and board sign-off with SAMA submission.
- The biggest timeline risk is rarely the technical controls themselves. It is the evidence collection, monitoring, and reporting overhead that a small team cannot sustain alongside building product.
- Governed AI Teammates can absorb that operational load, with your team keeping full authority over scope, permissions, and approvals.
Introduction
Most fintech founders in Saudi Arabia find out about the SAMA Cybersecurity Framework (CSF) the same way: a licensing requirement, an investor due diligence checklist, or a partner bank asking for proof of compliance before they will integrate. What follows is usually a scramble. Policies get written in a weekend. A vulnerability scan gets mistaken for a penetration test. Somebody spends three days manually screenshotting configurations for an auditor who will ask for the same evidence again next quarter.
None of that is a maturity problem. It is a capacity problem. SAMA CSF compliance is not hard because the controls are exotic. It is hard because a startup security team of one or two people is expected to produce the same evidence, monitoring, and board reporting that a bank builds with a full compliance department.
This guide lays out a realistic 18-month roadmap to SAMA CSF Level 3, the regulatory minimum every SAMA-supervised entity must reach, and where the work can be handed to something other than your already-stretched team.
What the SAMA CSF Actually Requires
The SAMA Cybersecurity Framework applies to every entity regulated by the Saudi Central Bank, including licensed fintechs, BNPL providers, and technology firms that process transactions or hold financial data on behalf of a SAMA-regulated institution. Compliance is not optional and it is not a one-time certificate. It is demonstrated through annual self-assessments and periodic supervisory reviews.
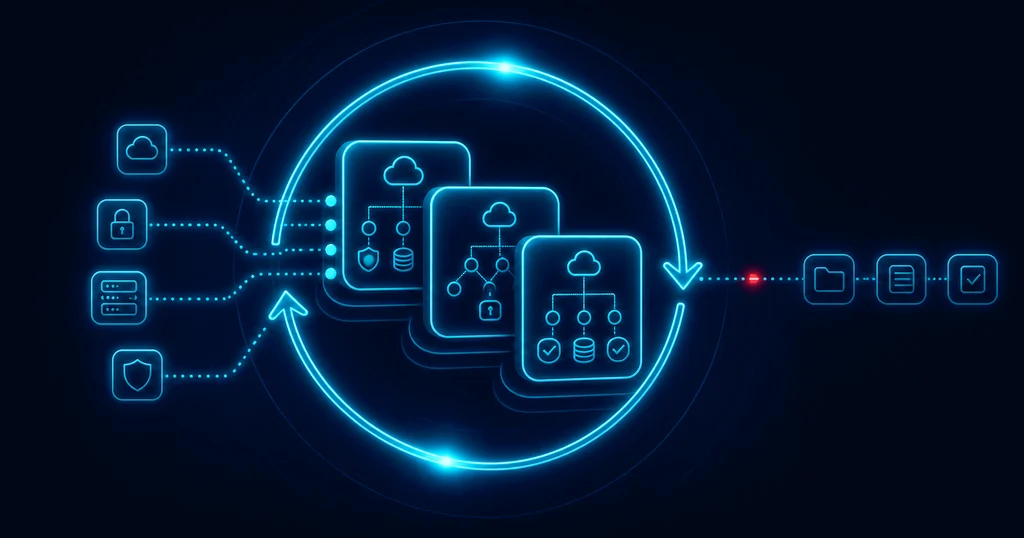
The framework groups its requirements into four broad areas:
Four Pillars, One Mandatory Floor
Every SAMA-regulated fintech — licensed startups, BNPL providers, and processors alike — is scored across four domains. Every control in scope must clear Level 3 to count.
Governance & Leadership
- Board accountability
- A designated CISO
- Approved cybersecurity strategy
- Regular reporting to the board
Risk Management & Compliance
- Risk classification
- Compliance monitoring
- Regulatory reporting
- Oversight of third-party risk
Operations & Technology
- Identity & access management
- Vulnerability management
- Incident response & network security
- Secure development & continuity
Third-Party Cybersecurity
- Vendor due diligence
- Ongoing partner assessment
- Cloud provider oversight
- Governance and leadership. Board accountability, a designated CISO, an approved cybersecurity strategy, and regular reporting to the board.
- Risk management and compliance. Risk classification, compliance monitoring, regulatory reporting, and oversight of third-party risk.
- Operations and technology. The technical backbone: identity and access management, vulnerability management, incident response, network security, secure development, and business continuity.
- Third-party cybersecurity. Due diligence and ongoing assessment of vendors, outsourcing partners, and cloud providers.
Every control across these areas is scored on a six-point maturity scale, from non-existent to optimised. SAMA sets Level 3, “defined,” as the mandatory floor. That means controls must be formally documented, board-approved, and actively monitored, not just written down somewhere and hoped for. A policy without evidence that it is followed does not clear Level 3.
Why 18 Months Is the Honest Number
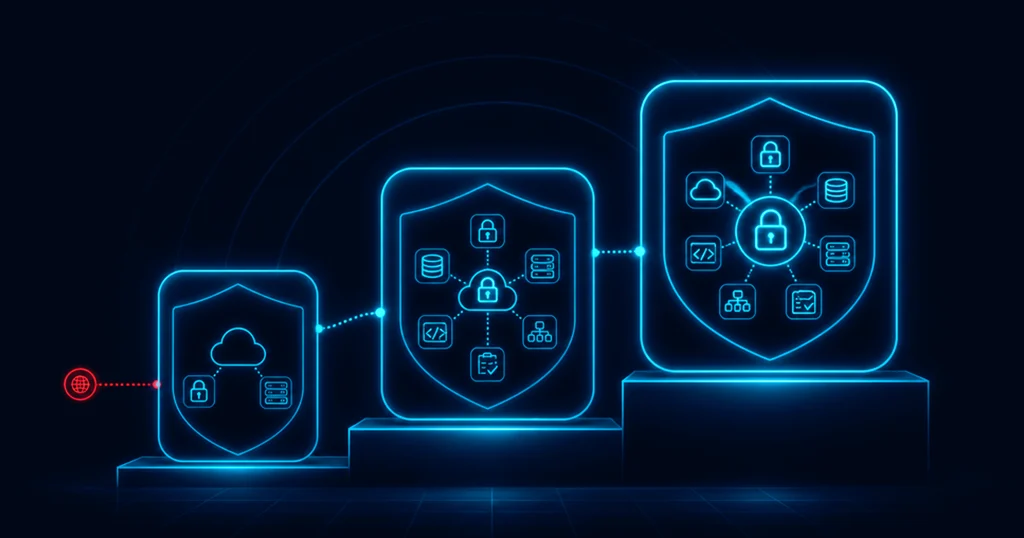
Startups that begin with little to no formal security program typically start at Level 0 or Level 1 across most domains. Reaching Level 3 from that starting point realistically takes nine to eighteen months of sustained work, and eighteen months is the more common outcome once you account for hiring lag, evidence accumulation, and the fact that a control cannot be claimed at Level 3 without first passing through Levels 1 and 2 in sequence.
Is 18 Months the Right Number
Startups can’t skip levels. A control can’t be claimed at Level 3 without first passing through Levels 1 and 2 — in sequence.
Little to no formal security program in place across most SAMA CSF sub-domains.
Documented, board-approved, and actively monitored — not policy on paper.
Fintechs that already hold ISO 27001 or SOC 2 certification can move faster because much of the technical control mapping already exists. Fintechs starting from scratch cannot skip steps, no matter how good their engineering team is at shipping product quickly. Compliance maturity and product velocity are different clocks.
The single most expensive mistake we see is skipping the gap assessment and going straight to buying tools or writing policy. Startups that do this consistently discover, at their first SAMA review, that they over-built in areas that were already fine and left the domains carrying the most risk untouched.
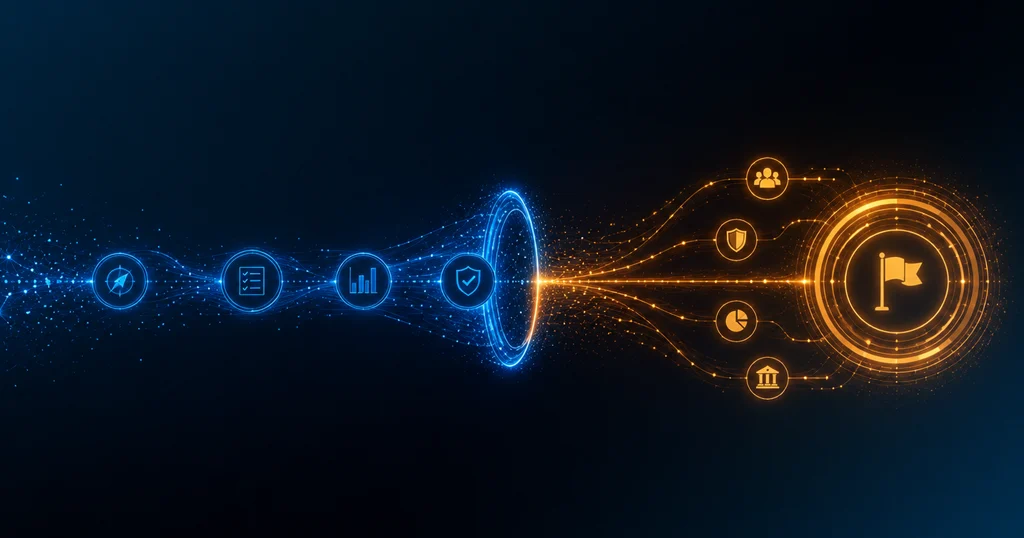
An 18-Month Roadmap for Fintech Startups
An 18-Month Path to Audit-Ready
Six phases, sequenced so governance, technical controls, and evidence maturity all land before independent testing begins.
Swipe to see all six phases
Baseline & Scope
- Map data flows against SAMA CSF sub-domains
- Score current maturity with evidence, not intent
- Rank every gap by remediation effort
Governance Foundations
- Appoint or designate a CISO
- Secure board approval for cyber strategy
- Set a board reporting cadence
Control Build-Out
- Formalise standards per sub-domain
- Implement access, logging & monitoring
- Extend controls into vendor contracts
Monitoring & Evidence
- Stand up compliance monitoring
- Run full internal self-assessments
- Close gaps before SAMA review
Independent Testing
- Commission full-scope pen testing
- Remediate findings and retest
- Retain before/after evidence
Board Sign-Off
- Finalise roadmap, secure sign-off
- Submit to SAMA, report quarterly
- Set recurring annual assessment
Months 0 to 2: Baseline and Scope
Before anything gets built, you need an accurate picture of where you stand. This phase should produce a scored gap register across every applicable sub-domain, not a general impression that “things are mostly okay.” Scoping matters here too: which sub-domains apply to your specific licence type, and where your data and payment flows actually put you in scope.
- Map business lines, systems, and data flows against SAMA CSF sub-domains
- Score current maturity per control with supporting evidence, not intent
- Flag every control below Level 3 and rank by remediation effort
Months 2 to 5: Governance Foundations
Governance is the domain fintechs most often underweight, because it produces no code and no dashboard. It is also the domain SAMA checks first. A board that has never seen a cybersecurity report will fail this section regardless of how strong the technical stack is.
- Appoint or formally designate a CISO
- Draft and secure board approval for a cybersecurity policy and strategy
- Establish a cybersecurity committee with a defined reporting cadence to the board
Months 4 to 10: Control Build-Out
This is the longest phase and runs largely in parallel with governance work. Technical and procedural controls across identity management, vulnerability management, incident response, network segmentation, secure development, and business continuity all need to move from Level 1 or 2 toward Level 3, with configuration records, access logs, and procedure documents to prove it.
- Formalise standards and procedures for each in-scope sub-domain
- Implement access controls, logging, and monitoring with retained evidence
- Extend security requirements into vendor and cloud contracts, and secure any required regulatory approval for cloud usage
Months 9 to 14: Monitoring and Evidence Maturity
A control that exists but is never checked is not at Level 3. This phase is where startups build the habit of ongoing compliance monitoring: tracking exceptions, running internal audits, and keeping an evidence trail current instead of reconstructed under deadline pressure.
- Stand up recurring compliance monitoring and exception tracking
- Run internal self-assessments against the full framework, not a sample
- Close residual gaps identified during monitoring before they surface in a SAMA review
Months 12 to 16: Independent Testing
SAMA expects penetration testing as evidence that controls actually hold up under attack, not just on paper. This needs to cover the full regulated environment, including APIs, mobile applications, and cloud infrastructure, and it needs a documented remediation and retest cycle. A scan report filed and forgotten will not satisfy an assessor.
- Commission full-scope penetration testing by qualified practitioners
- Remediate findings and retest to prove the fix held
- Retain before-and-after evidence as part of the audit trail
Months 15 to 18: Board Sign-Off and Submission
The roadmap itself must be approved by the board and submitted to SAMA, with quarterly progress reports continuing until full compliance is reached. This is not paperwork at the end. It is the formal handoff of everything built in the previous fifteen months into a form SAMA can review.
- Finalise the remediation roadmap and secure board sign-off
- Submit to SAMA and establish the quarterly reporting cadence
- Set the recurring cycle for annual self-assessment and continuous evidence collection
Common Mistakes Fintech Startups Make on the SAMA Journey
- Treating a written policy as a finished control. SAMA assessors look for evidence of consistent implementation, not just a signed PDF.
- Scoping penetration testing to the public website only. APIs, mobile apps, and cloud infrastructure are all in scope and all get checked.
- Leaving the board out of the loop. Governance failures show up regardless of how strong your technical stack is.
- Skipping the gap assessment. Building controls before scoping wastes budget on areas that were already fine.
- Underestimating third-party and cloud requirements. Vendor contracts, security assessments, and cloud approvals are frequently the most underbuilt domain in a startup’s first year.
It’s Rarely the Controls. It’s the Evidence Chasing.
Ask any fintech security lead what eats the most time on this roadmap — the answer is rarely the technical controls:
- Pulling screenshots and reconciling logs across tools
- Chasing sign-offs from every stakeholder involved
- Rewriting the same status update for the third audience this month
- Stitching one compliance picture together across five different consoles
That’s the grunt work — and exactly the toil that leads to burnout on small security teams, and the reason startups fall behind schedule even when their controls are sound.
Governed Defense, Powered by Offense.No More Grunt Work. No More Burnout.
GRC AI Teammate
- Owns controls, compliance posture & evidence collection
- Handles audit readiness and trust reporting
- Executes inside the scope, permissions & approvals you define
- Doesn’t replace your CISO or board — frees them for judgment calls
Red AI Teammate
- Runs continuous, approved-scope adversary simulation
- Used for the testing phase of the roadmap
- Feeds results into what defenses need to harden next
- The teammate that attacks teaches the teammate that defends
Vulnerability Risk Acceptance and Exception Workflows
How security teams document risk acceptance, run exception governance, and keep the audit trail clean.
Read more CybersecurityHow to Implement Risk-Based Vulnerability Management
A step-by-step look at what it actually takes to run risk-based vulnerability management, from asset criticality to board reporting.
Read more Infrastructure SecurityHow to Communicate Vulnerability Risk to Executives
A practical breakdown of how to translate risk data into a story executives and boards will actually act on.
Read moreFAQs
How long does SAMA CSF compliance actually take for a fintech startup?
What does Level 3 actually mean in practice?
Do we need ISO 27001 as well as SAMA CSF?
Can a two-person security team realistically hit this timeline without a large hire?
What happens if a startup misses its self-imposed roadmap timeline?
Conclusion
Reaching SAMA CSF Level 3 is achievable for a fintech startup in eighteen months, but only if the roadmap accounts for where the real time goes: not the technical build-out, but the governance, evidence, and monitoring work that never stops once you start. Secure.com provides governed AI security teammates that attack, harden, and prove defensive outcomes, above the stack you already own, with your team setting the rules and approving consequential action. Attack. Harden. Prove. Repeat.